Search results for tag #selfhosting
There has never been a better time to introduce young French people to the wonderful world of decentralized social networks and - optional - #selfhosting.
An accidental ad for the #Fediverse, exhibit A: https://www.politico.eu/article/french-government-mulled-blocking-social-network-amid-protests/
I’d like to start experimenting self-hosting with a Raspberry Pi + YunoHost, but I’m struggling to wrap my head around the security risks.
If I expose it to the internet via my home router, this could potentially put all devices on my family’s home Wi-Fi at risk.
Any security experts who can share advice on a safe setup for a beginner? 🙏
All tips and suggestions are much appreciated! #selfhosting

Automated watch of vulnerabilities affecting my infrastructure
In this blog post, I share how I get notifications, tickets and fix pull requests for newly published vulnerabilities affecting my infrastructure
https://dataswamp.org/~solene/2026-10-23-automated-vulnerability-watch.html
gemini://perso.pw/blog/articles/automated-vulnerability-watch.gmi
Meine E-Books synchron auf allen Geräten (ohne Amazon)
► Wie sich dieser Channel finanziert: https://www.youtube.com/watch?v=xWLRoMP3rLU
► Links aus dem Video:
Calibre-Web Automated (CWA):
https://github.com/crocodilestick/Calibre-Web-Automated
Kavita (Alternative zu CWA):
https://github.com/Kareadita/Kavita
KOReader:
https://koreader.rocks/
KOReader – Installationsanleitungen für Kindle, Kobo/Tolino, PocketBook & Android:
https://github.com/koreader/koreader-sync-server
KOReader Sync Server (KOSync):
https://github.com/koreader/koreader-sync-server
kosync-cwa-bridge:
https://github.com/ericchansen/kosync-cwa-bridge
Readest (für iPhone & iPad):
https://readest.com/
CrossPoint Reader (Firmware für Xteink X3/X4, Flashen direkt im Browser):
https://crosspointreader.com/
Kindle Modding Wiki (Jailbreak & KOReader auf dem Kindle):
https://kindlemodding.org/
Cloudflare Tunnel:
https://developers.cloudflare.com/cloudflare-one/networks/connectors/cloudflare-tunnel/
Tailscale:
https://tailscale.com/
Onleihe:
https://www.onleihe.de/
► c't 4004 - der c't-3003-Podcast: https://ct-3003.podigee.io/
► DER 3003-HYPE-NEWSLETTER: https://ct.de/hype
► Kapitelmarker:
0:00 Intro
1:14 Das Problem der vielen Geräte
2:55 Was MUSS der eBook-Server können?
4:27 Auf welchen Readern geht das?
5:26 Calibre-Web Automated (Bibliothek)
7:24 OPDS (Open Publication Distribution System)
9:07 KOSync (Lesestand synchronisieren)
14:22 Fazit
► Alle Newsletter von Heise: https://www.heise.de/newsletter/
► Hier geht es zum c't-WhatsApp-Kanal: https://www.whatsapp.com/channel/0029VaCUFFEInlqYnQg2lb0h
► Lukas auf LinkedIn: https://www.linkedin.com/in/lukas-rumpler/
► Lukas auf Bluesky: https://bsky.app/profile/lukasrumpler.de
► c't Magazin: http://ct.de
► und TOTAL CRAZY auf Papier! Überall wo es Zeitschriften gibt!
► Credits:
Konzept & Redaktion: Lukas Rumpler
Schnitt: Pascal Schewe
Host: Lukas Rumpler
It's about ownership, not money...but yeah. Just smack me next time 😆 #homelab #selfhosted #selfhosting
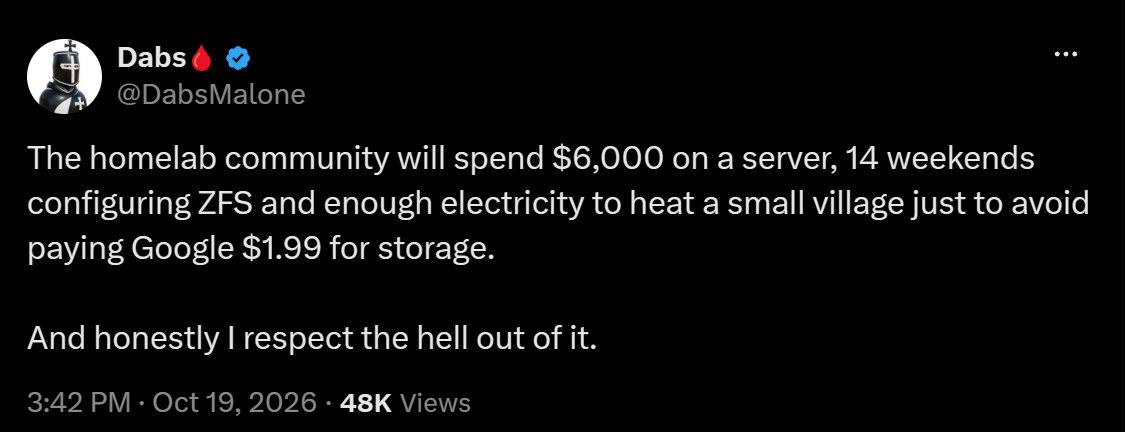
Alt...
@DabsMalone
The homelab community will spend $6,000 on a server, 14 weekends
configuring ZFS and enough electricity to heat a small village just to avoid
paying Google $1.99 for storage.
And honestly | respect the hell out of it.
3:42 PM - Oct 19, 2026 - 48K Views
🚨 A heads-up for anyone running #WordPress, #Moodle, #Nextcloud or other PHP-based services.
PHP has confirmed two critical vulnerabilities, both rated 9.2/10. Fixes are scheduled for today, 21 October, at 14:00 UTC.
Prepare to patch PHP, not just your applications. CERT-EU advises considering temporary isolation of public-facing services if prompt patching isn't possible.
It sounds pretty bad. Affected versions are not yet confirmed but I've heard 5.4+
@ironicbadger A real restore onto different hardware is the only test that proves a backup. Fifteen minutes is fast. Did the Zigbee and Bluetooth radios come across cleanly on the ZimaBoard, or did those need re-pairing?
Mein #PeerTube Server hat endlich ein Publikum! Leider sind es KI-Crawler. Die schauen alles, liken nichts und kommen morgen wieder. Ich glaube, ich habe meine treuesten Fans gefunden.
#fediverse #ki #selfhosting #foss #schicksalsjahreeineskaisers

Big step today. Powered down the last of my self-hosted infra at the house which meant my Home Assistant went bye bye. Can’t have that.
good golly i do love home assistant os
I took a full backup and downloaded it before taking my server offline. uploaded it to a fresh install i threw onto a zimaboard that will allow me to limp along for the next 2 weeks or so as i need to.
i'm back up in 15 mins literally exactly as it was before. amaze.


Seit heute bin ich zufriedener User von Rust Desk zum Fernsteuern anderer Geräte wie Server, PCs oder Smartphones.
Somit habe ich kein Bedarf mehr nach AnyDesk, das nur noch eine Verbindung von 5 Minuten erlaubt und danach die Verbindung abbricht.
Ich betreibe ohnehin einen VPS-Server und nun habe ich dort einen RustDesk-Server als Docker Container installiert. Alles funktioniert ohne Limits. Super gut!
#rustdesk #opensource #selfhosted #selfhosting #vps #anydesk #teamviewer
Finally turned attention to getting Immich up and running tonight. I like it, seems snappy enough with tens of thousands of photos imported.
The Immich website has a handy form driven page for generating a docker compose file so it took like 30 seconds to get it running once mutated to follow my way of doing things on my server (persistent storage, naming, cert proxy, etc).
I struggled a bit with using the Immich command line tool to import my photo collection and in the process of trying to figure out why --recursive didn't work, stumbled upon the immich-go project on github. It's also a command line tool and works very well; immediately was able to recursively import photos, etc. Compiles cleanly on Alpine Linux (ofc, it's just golang).
Immich-go has a migrate function that allows you to connect to one Immich server and copy the files to another Immich server (but no 'delete source' as far as I could tell).
I set up a second Immich instance on a different port and started to use the migrate function to finally start moving all the photos of my computer electronics and vehicle technical projects out of the whole household's photo collection. My wife will appreciate that. Ha. Managed to split out 2026-2025, only ~25 more years to go. Ugh.
Anyway, Immich (the server) and Immich-go (the CLI tool) are cool. Recommended.
Fun!
#immich #immichgo #AlpineLinux #cli #photography #photos #HomeLab #SelfHosting #SelfHosted

New on the blog: Self-Hosted AI.
Qwen 3.8 27B on a rented RTX PRO 6000 Blackwell, one shell command, ~150 tokens per second. For most of my everyday coding, it is simply good enough now.
Also: what "self-hosted" really means on someone else's GPU. You swap trust in an AI vendor for trust in an infrastructure provider. Not zero trust, but a question I already know how to answer.
https://blog.hofstede.it/self-hosted-ai-qwen-38-on-a-rented-blackwell-at-150-tokens-per-second/
I just had a thought. Some people talk about #SelfHosting and #Homelabs as some prepper like thing for weird people. I want to change that, as it certainly doesn't reflect how I feel about my mailserver, my various web servers and other services I run myself.
And that's where the thought comes in. From now on I will call it:
#PersonalComputing instead (or again, depending on your age :)
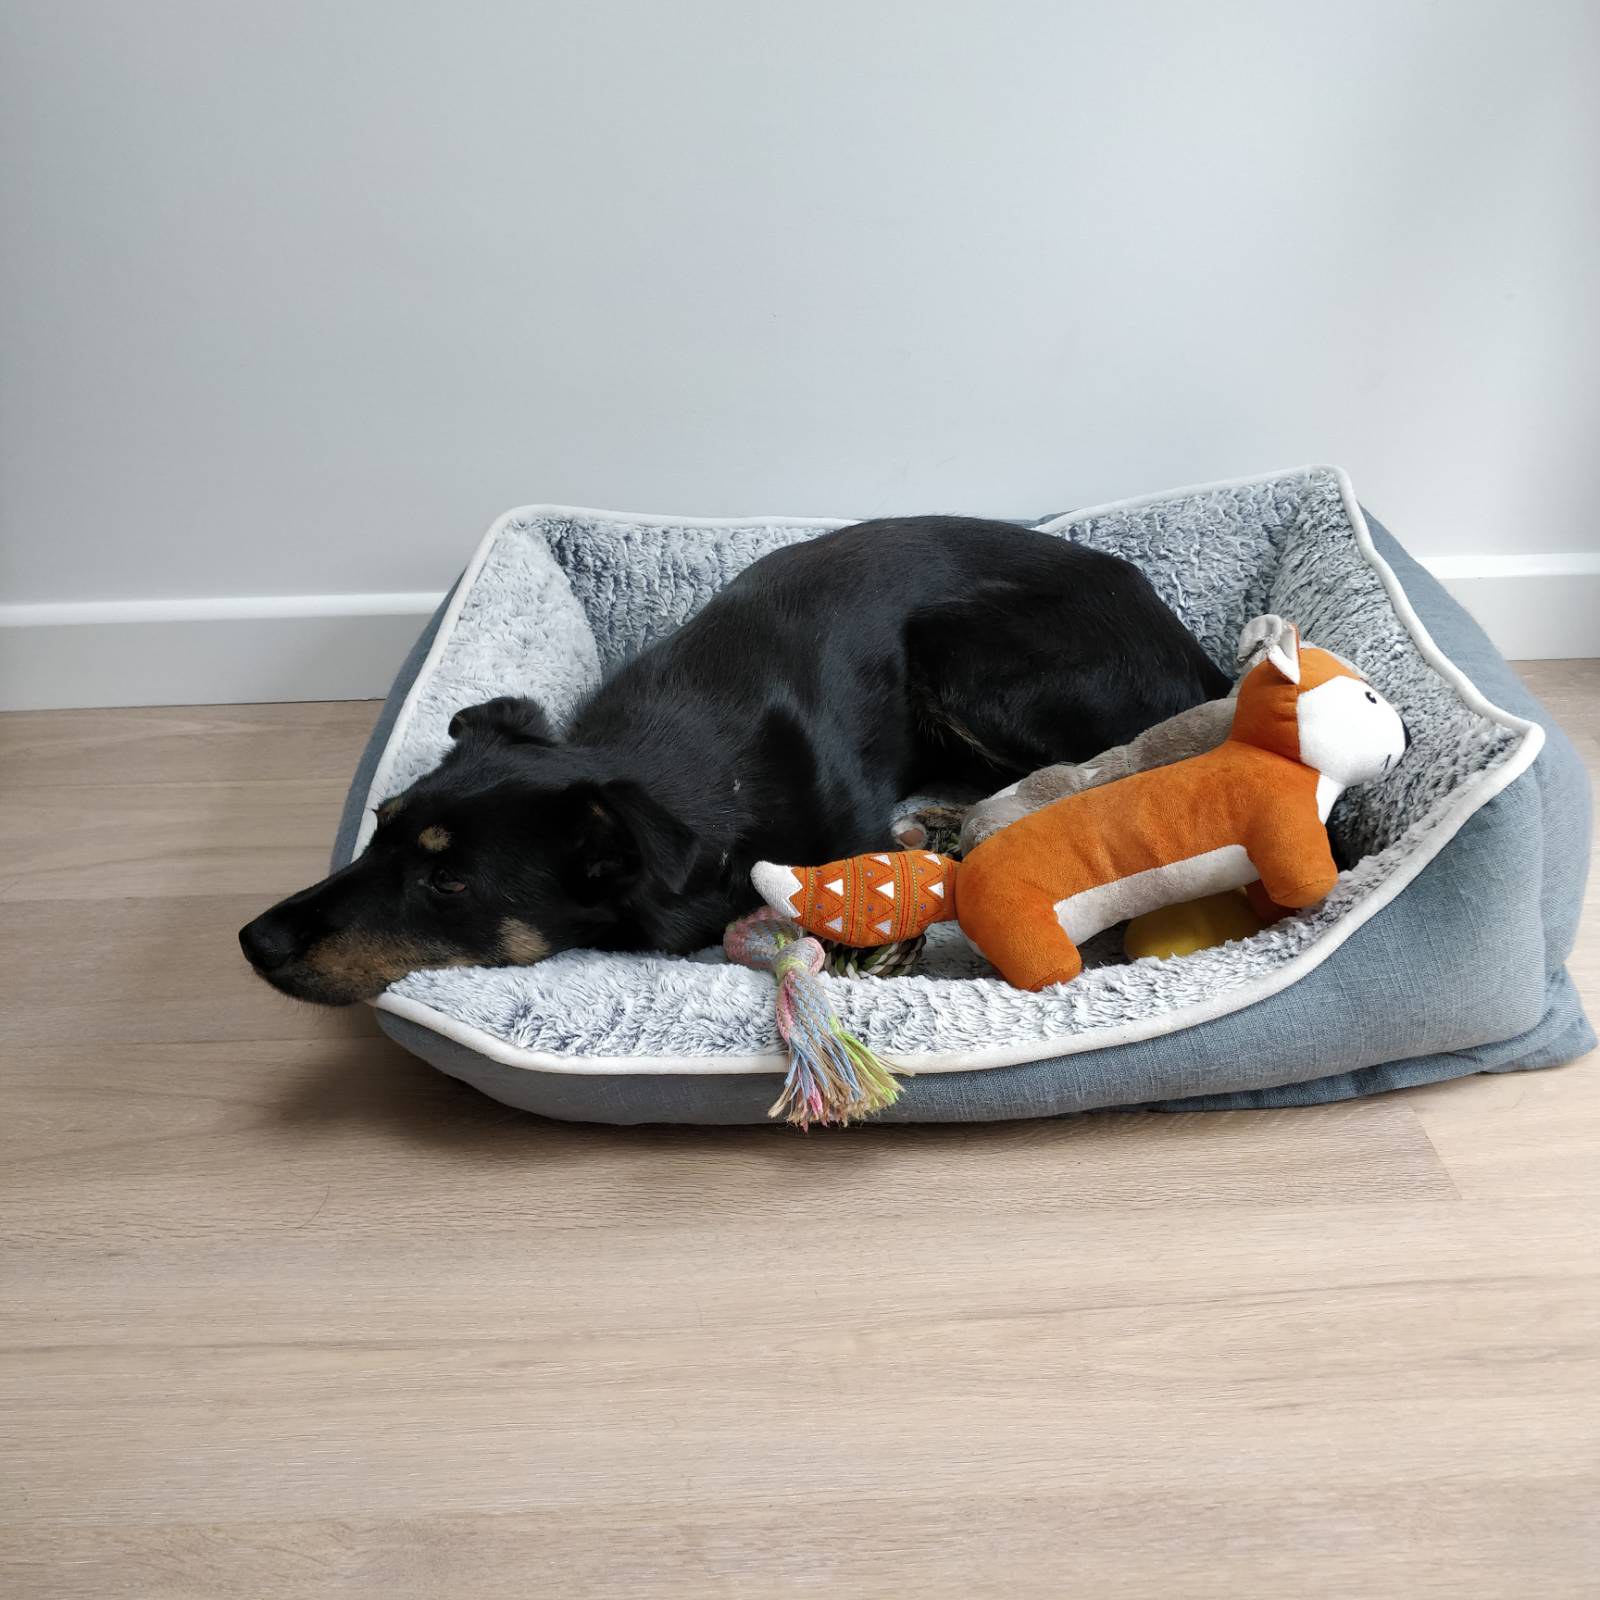
Hi everyone from my littlefedi instance, this is my first test post with a media file.
This is one of my dogs when she was very young
Alt...
a medium size black dog lying in a white and blue bed. Inside the bed is some of her toys, the one in the foreground is a little orange fox. The wall behind is white and the floor is a light coloured.wood

Wer den Bildschirm unserer Kunden sieht, ist eine Vertrauensfrage. Wessen Server die Sitzung vermittelt, ebenso. Deshalb hosten wir RustDesk selbst. Quelloffen, in unserer Hand, keine Vermittlung über Dritte.
Der Client liegt bei uns zum Download bereit, Windows, macOS und Linux, vorkonfiguriert. Starten, Kennung durchgeben, Anfrage bestätigen. Ohne Bestätigung keine Verbindung. Betrifft weiterhin nur die Clients, Serverwartung läuft wie gehabt.
#Fernwartung #SelfHosting #OpenSource #Datenschutz #ITSicherheit

Mastodon als Mailrelay: nicht Opfer, sondern Waffe
496 Bestätigungsmails an fremde Adressen: wie mein Mastodon-Server zum Werkzeug eines Cyberkriminellen wurde.
https://ingo.lantschner.name/post/2026-09-18_mailrelay-mastodon/
@zoul, @antars, @admin, @tealk, @Mme_de_Faune, @b2c, @SunDancer, @spielleitung, @pfitzer, @eggipedia
#Fediverse #Mastodon #Sicherheit #ITSecurity #CyberSecurity #Selfhosting #Mailbombing #Registrationbombing #bpSpam #Spam #PeerTube #SozialeMedien
Hm. Ich glaube ich will ein #HomeLab bauen.
Mal ein druckbares Gehäuse suchen und einfach beginnen.
#3D #3dprinting #DYI #Selfhosting
Quick heads-up for other Mastodon admins: this registration spam wave isn't over yet.
On lsbt.me, we first saw a flood of API registrations using Python/aiohttp. The telltale signs were usernames following the pattern bp plus 16 hex characters, and the sign-up reason was always "Automated protocol deliverability probe". A narrow block on that user agent stopped the first wave.
Today, however, five new registrations came in with the same usernames and the same sign-up reason. This time the bot simply identified itself as Chrome 126. That's exactly why a user agent is only useful as a short-term filter. It's a header the client can set to anything.
The requests go to POST /api/v1/accounts. This endpoint lets client apps create a new local account directly in the app. No app needs it for OAuth connections to existing accounts. #FediSuite doesn't use it either. It registers itself via /api/v1/apps, obtains consent via /oauth/authorize, and then works with a user token. Regular sign-up through the Mastodon website is also handled separately via POST /auth.
So I've completely disabled API account creation on lsbt.me. Web sign-up, OAuth, and existing clients keep working as before. Anyone who wants a new account just signs up once on the web as usual and can then use any client.
If you'd also rather not offer this optional native sign-up path, you can add the following to your Nginx server block, before the general location / block. The example assumes the @proxy location that many Mastodon Nginx configs already include:
location = /api/v1/accounts {
  limit_except GET {
    deny all;
  }  try_files $uri @proxy;
}
This returns a 403 only for POST /api/v1/accounts. The read-only GET endpoint remains reachable. As always, run nginx -t afterwards and only reload once the test passes.
#Mastodon #Fediverse #MastoAdmin #FediAdmin #FediMod #FediBlock #Moderation #Registration #Spam #Nginx #SelfHosting #SysAdmin #ActivityPub
Kurzer Hinweis an andere Mastodon-Admins: Diese Registrierungs-Spam-Welle ist noch nicht überstanden.
Bei lsbt.me kamen zunächst massenhaft API-Registrierungen mit Python/aiohttp rein. Auffällig waren Nutzernamen nach dem Muster bp plus 16 Hex-Zeichen und als Antragstext immer Automated protocol deliverability probe. Eine enge Sperre auf diesen User-Agent hat die erste Welle gestoppt.
Heute kamen trotzdem fünf neue Registrierungen mit denselben Nutzernamen und demselben Antragstext. Der Bot gab sich diesmal einfach als Chrome 126 aus. Genau deshalb taugt ein User-Agent nur als kurzfristiger Filter. Er ist ein frei wählbarer Header.
Die Requests laufen über POST /api/v1/accounts. Dieser Endpoint erlaubt Client-Apps, einen neuen lokalen Account direkt in der App anzulegen. Für OAuth-Verbindungen bestehender Accounts braucht ihn keine App. Auch #FediSuite nutzt ihn nicht. Sie registriert sich über /api/v1/apps, holt die Zustimmung über /oauth/authorize und arbeitet danach mit einem User-Token. Die normale Registrierung über die Mastodon-Webseite läuft ebenfalls getrennt über POST /auth.
Ich habe die API-Kontoerstellung auf lsbt.me deshalb komplett abgeschaltet. Webregistrierung, OAuth und bestehende Clients laufen unverändert weiter. Wer einen neuen Account möchte, registriert sich einmal ganz normal wie bisher im Web und kann danach jeden Client nutzen.
Falls ihr diesen optionalen Native-Sign-up-Weg ebenfalls nicht anbieten wollt, könnt ihr in eurem Nginx-Serverblock vor dem allgemeinen location /-Block Folgendes ergänzen. Das Beispiel setzt den in vielen Mastodon-Nginx-Configs vorhandenen @proxy voraus:
location = /api/v1/accounts {
  limit_except GET {
    deny all;
  }  try_files $uri @proxy;
}
Damit erhält nur POST /api/v1/accounts ein 403. Der lesende GET-Endpoint bleibt erreichbar. Danach wie immer nginx -t und erst bei erfolgreichem Test reloaden.
#Mastodon #Fediverse #MastoAdmin #FediAdmin #FediMod #FediBlock #Moderation #Registration #Spam #Nginx #SelfHosting #SysAdmin #ActivityPub
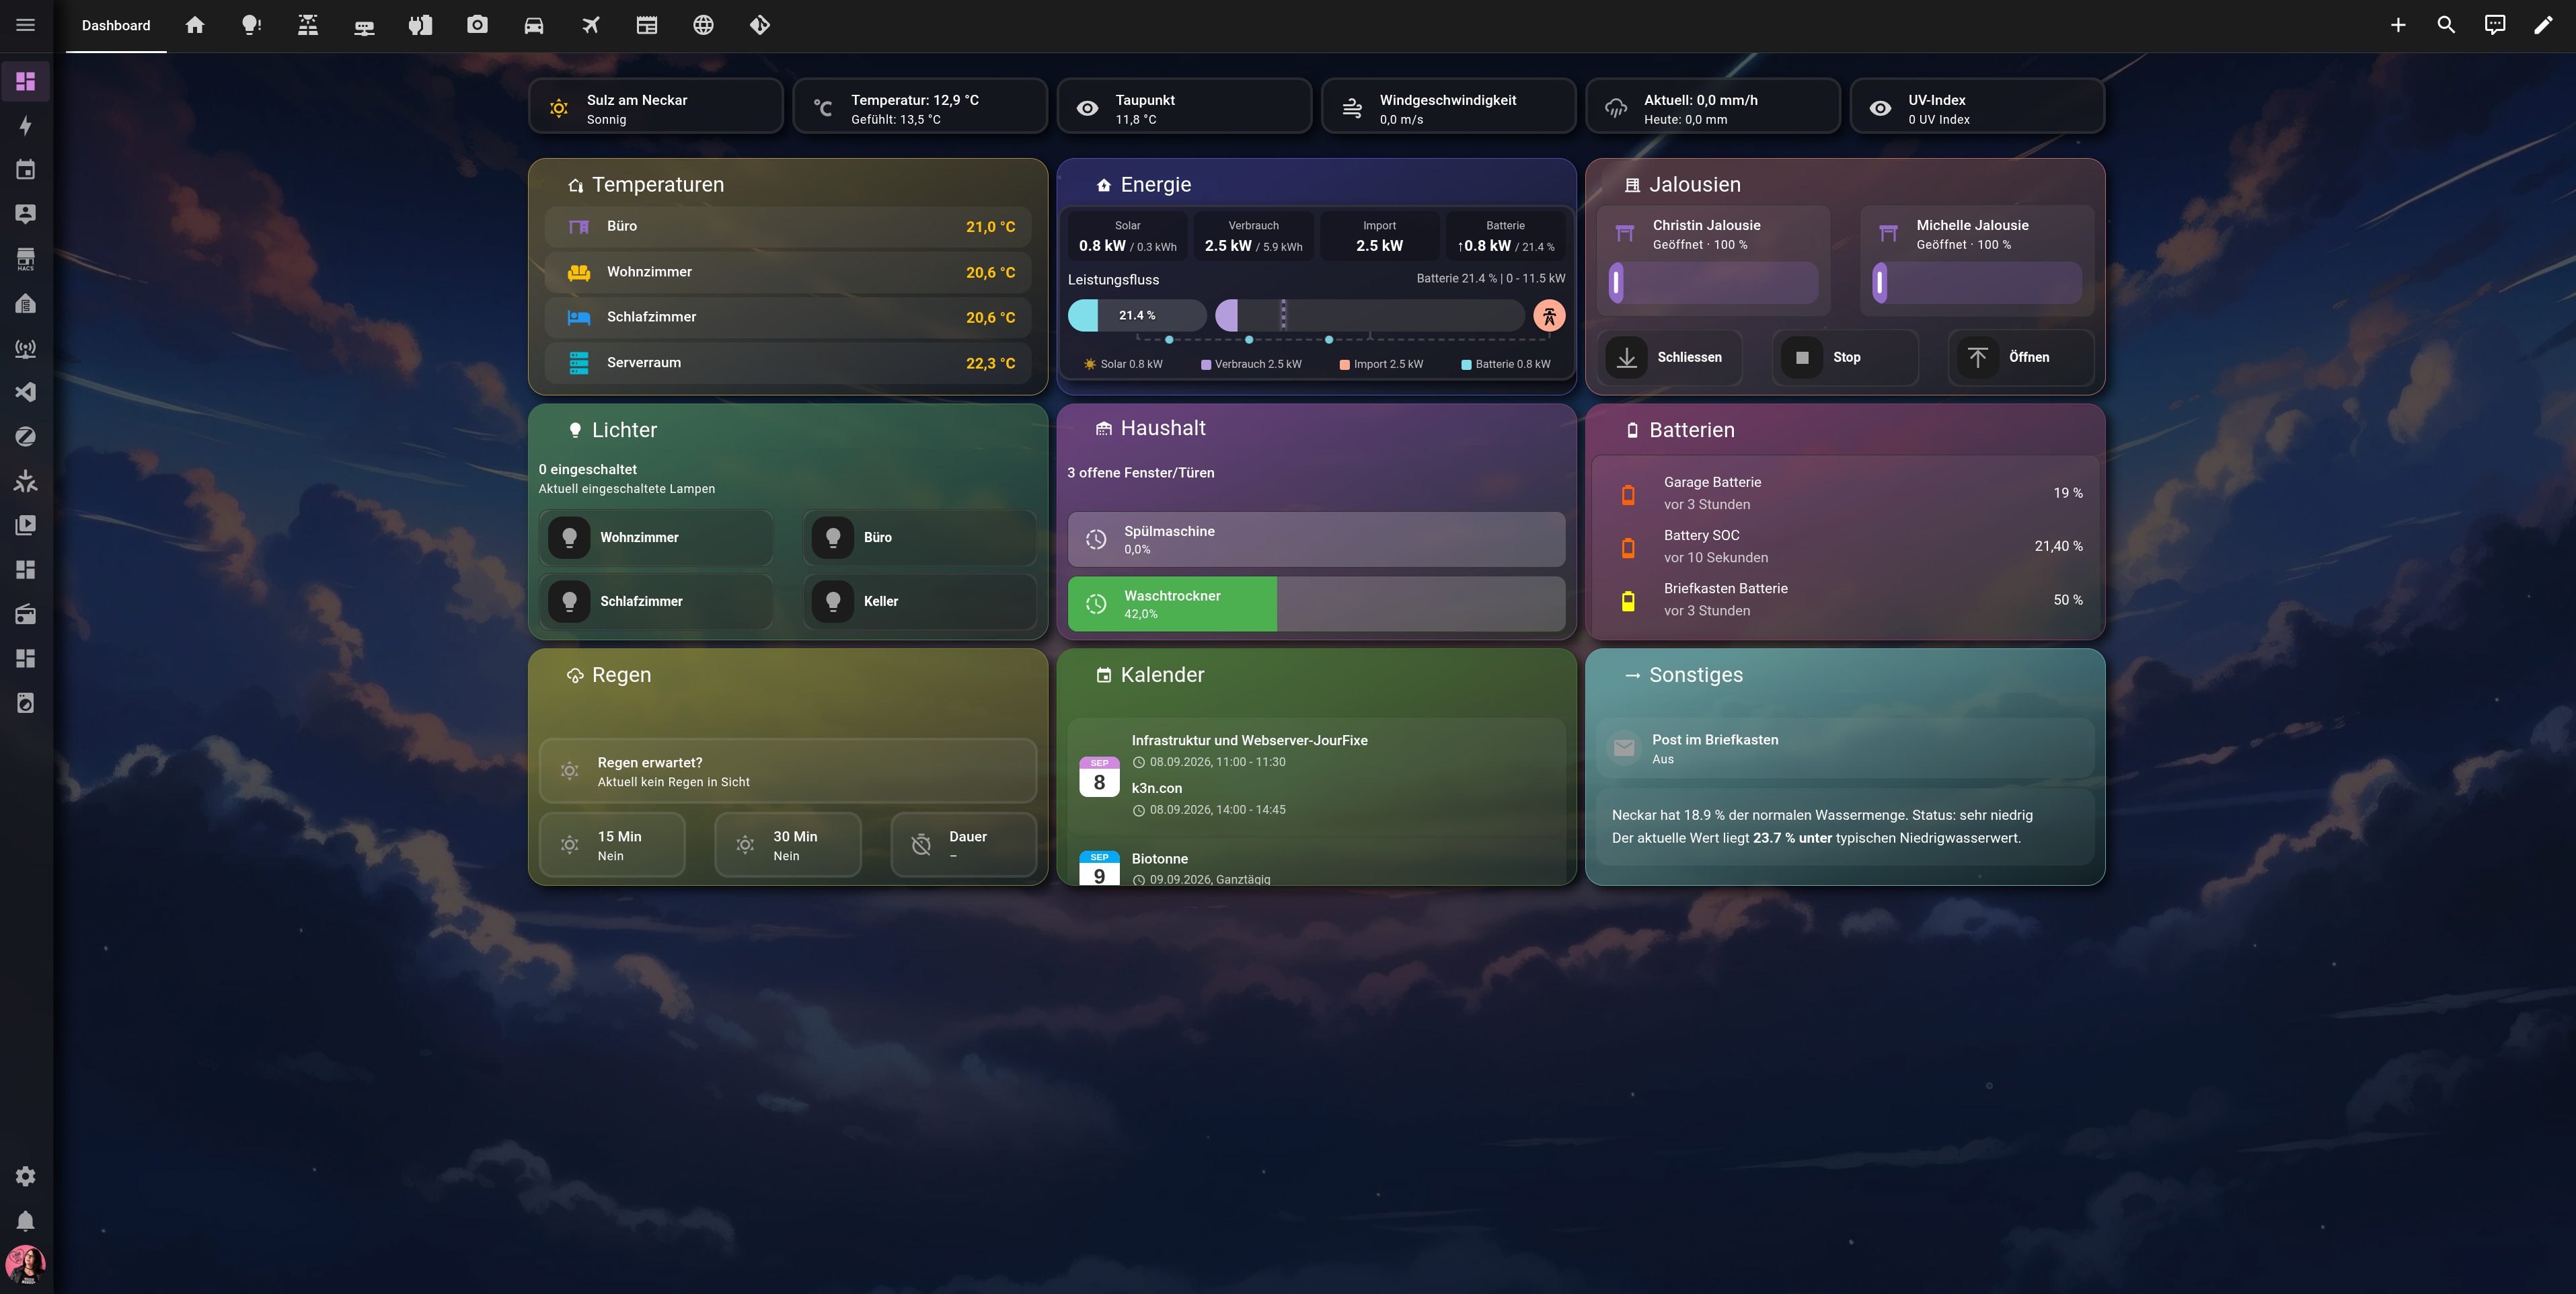
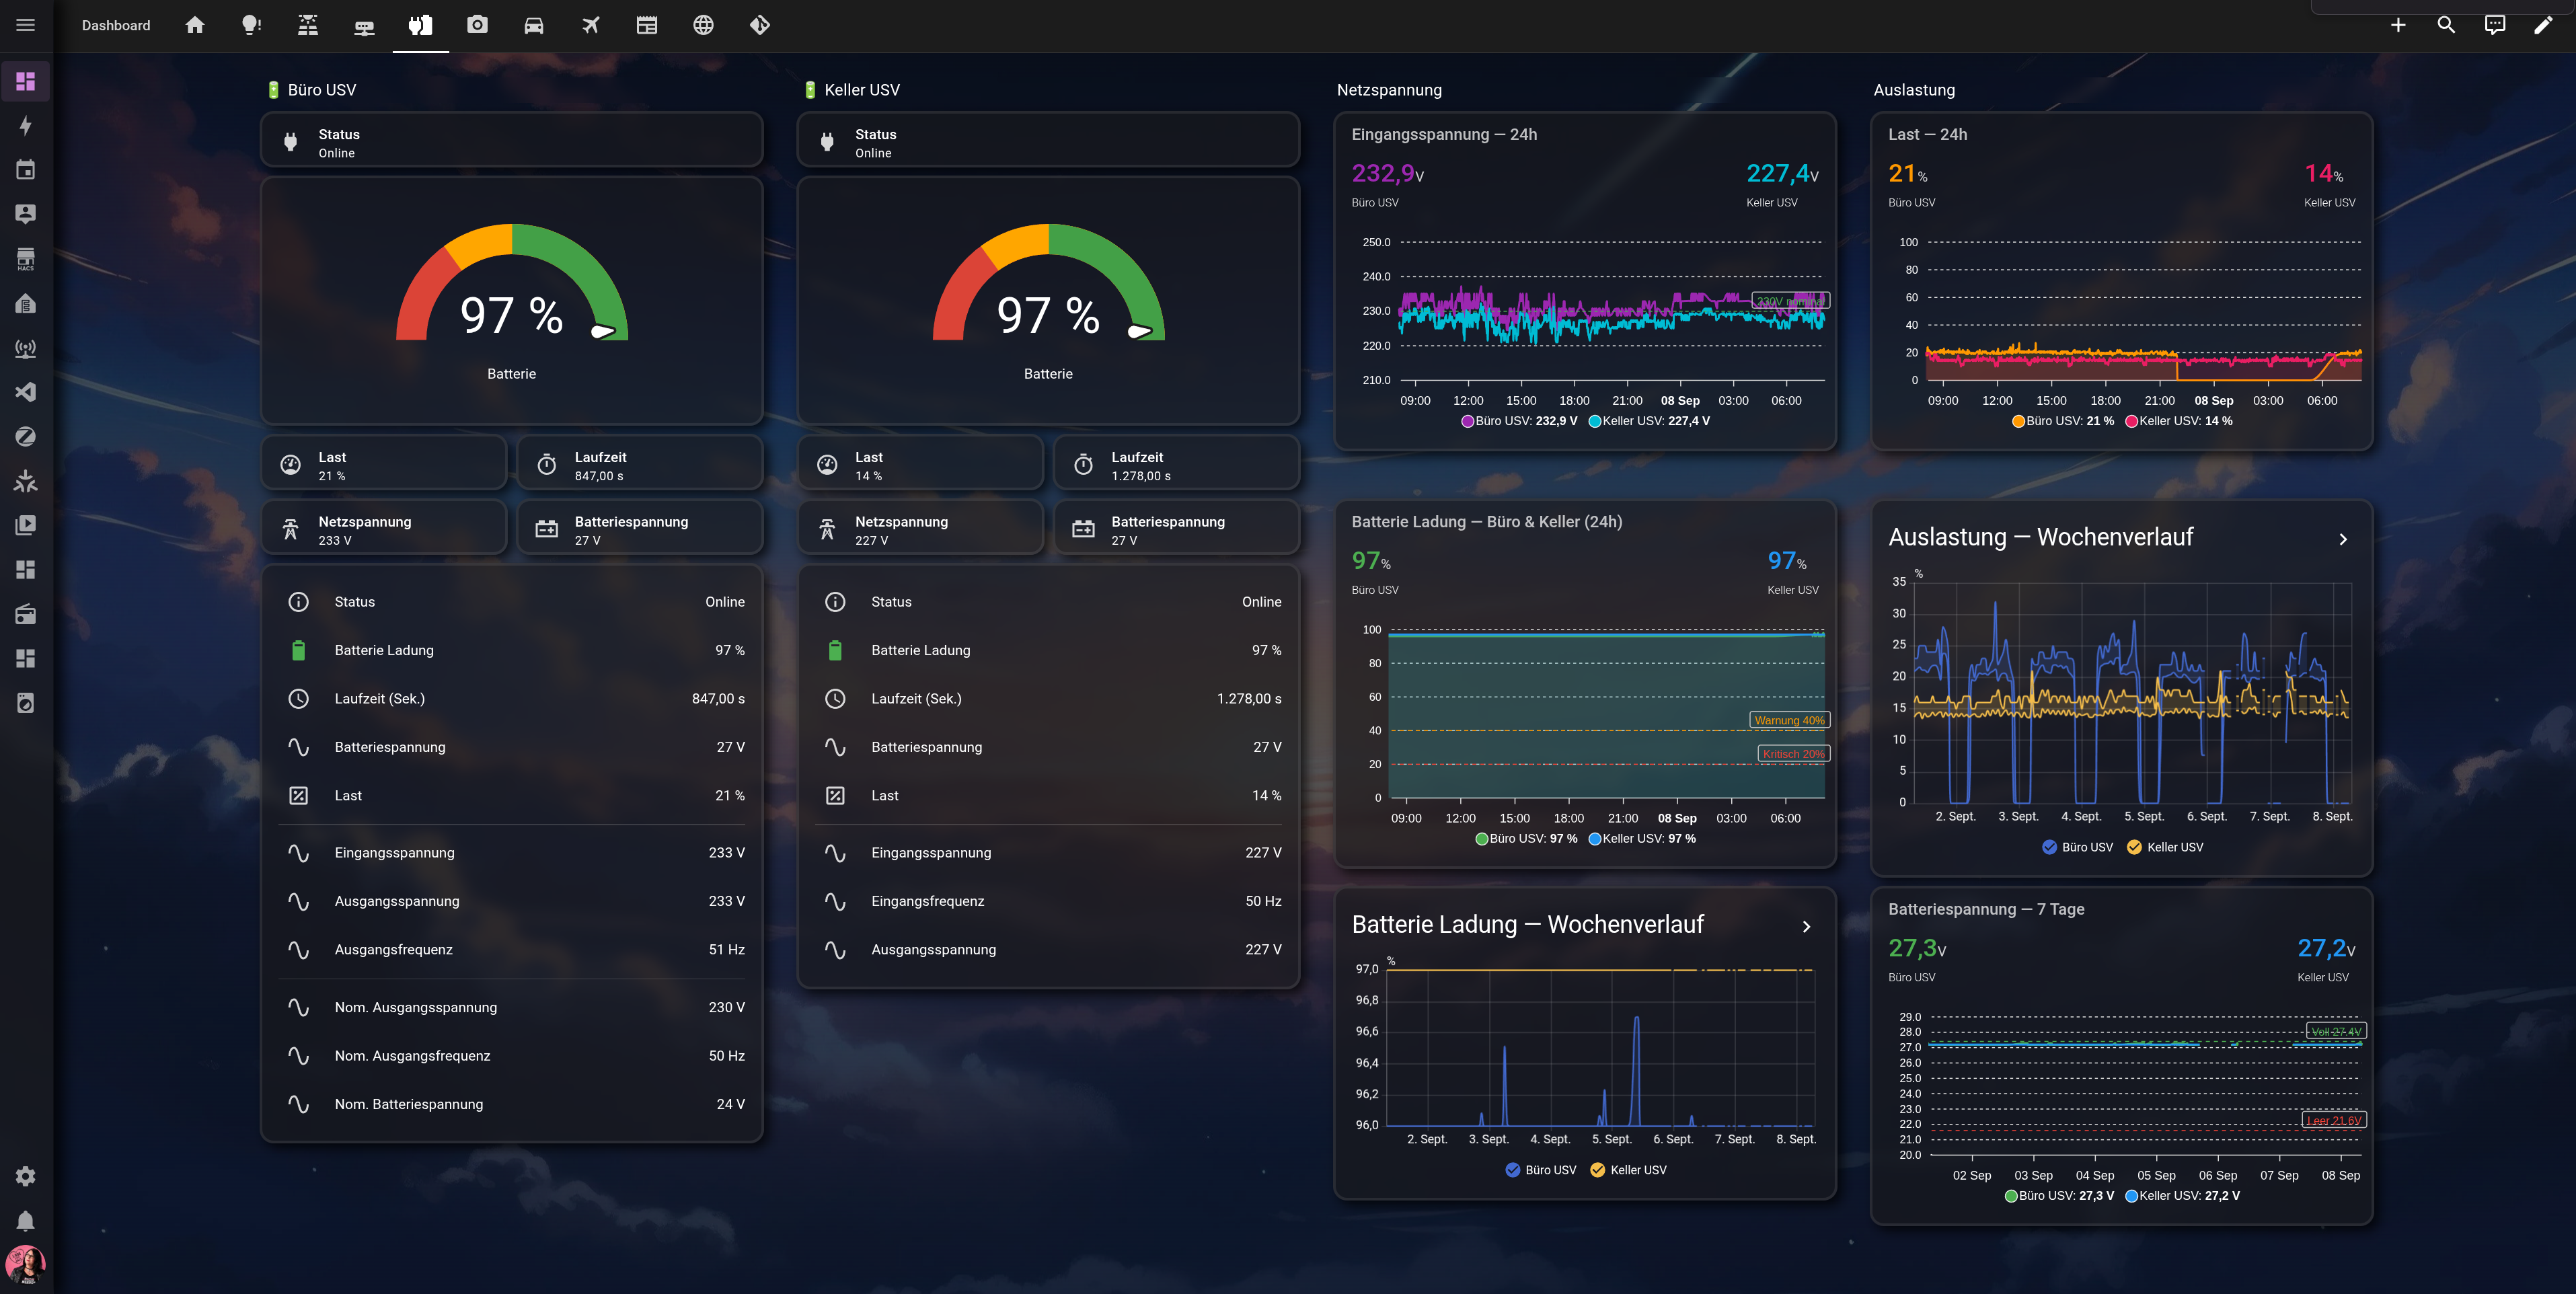
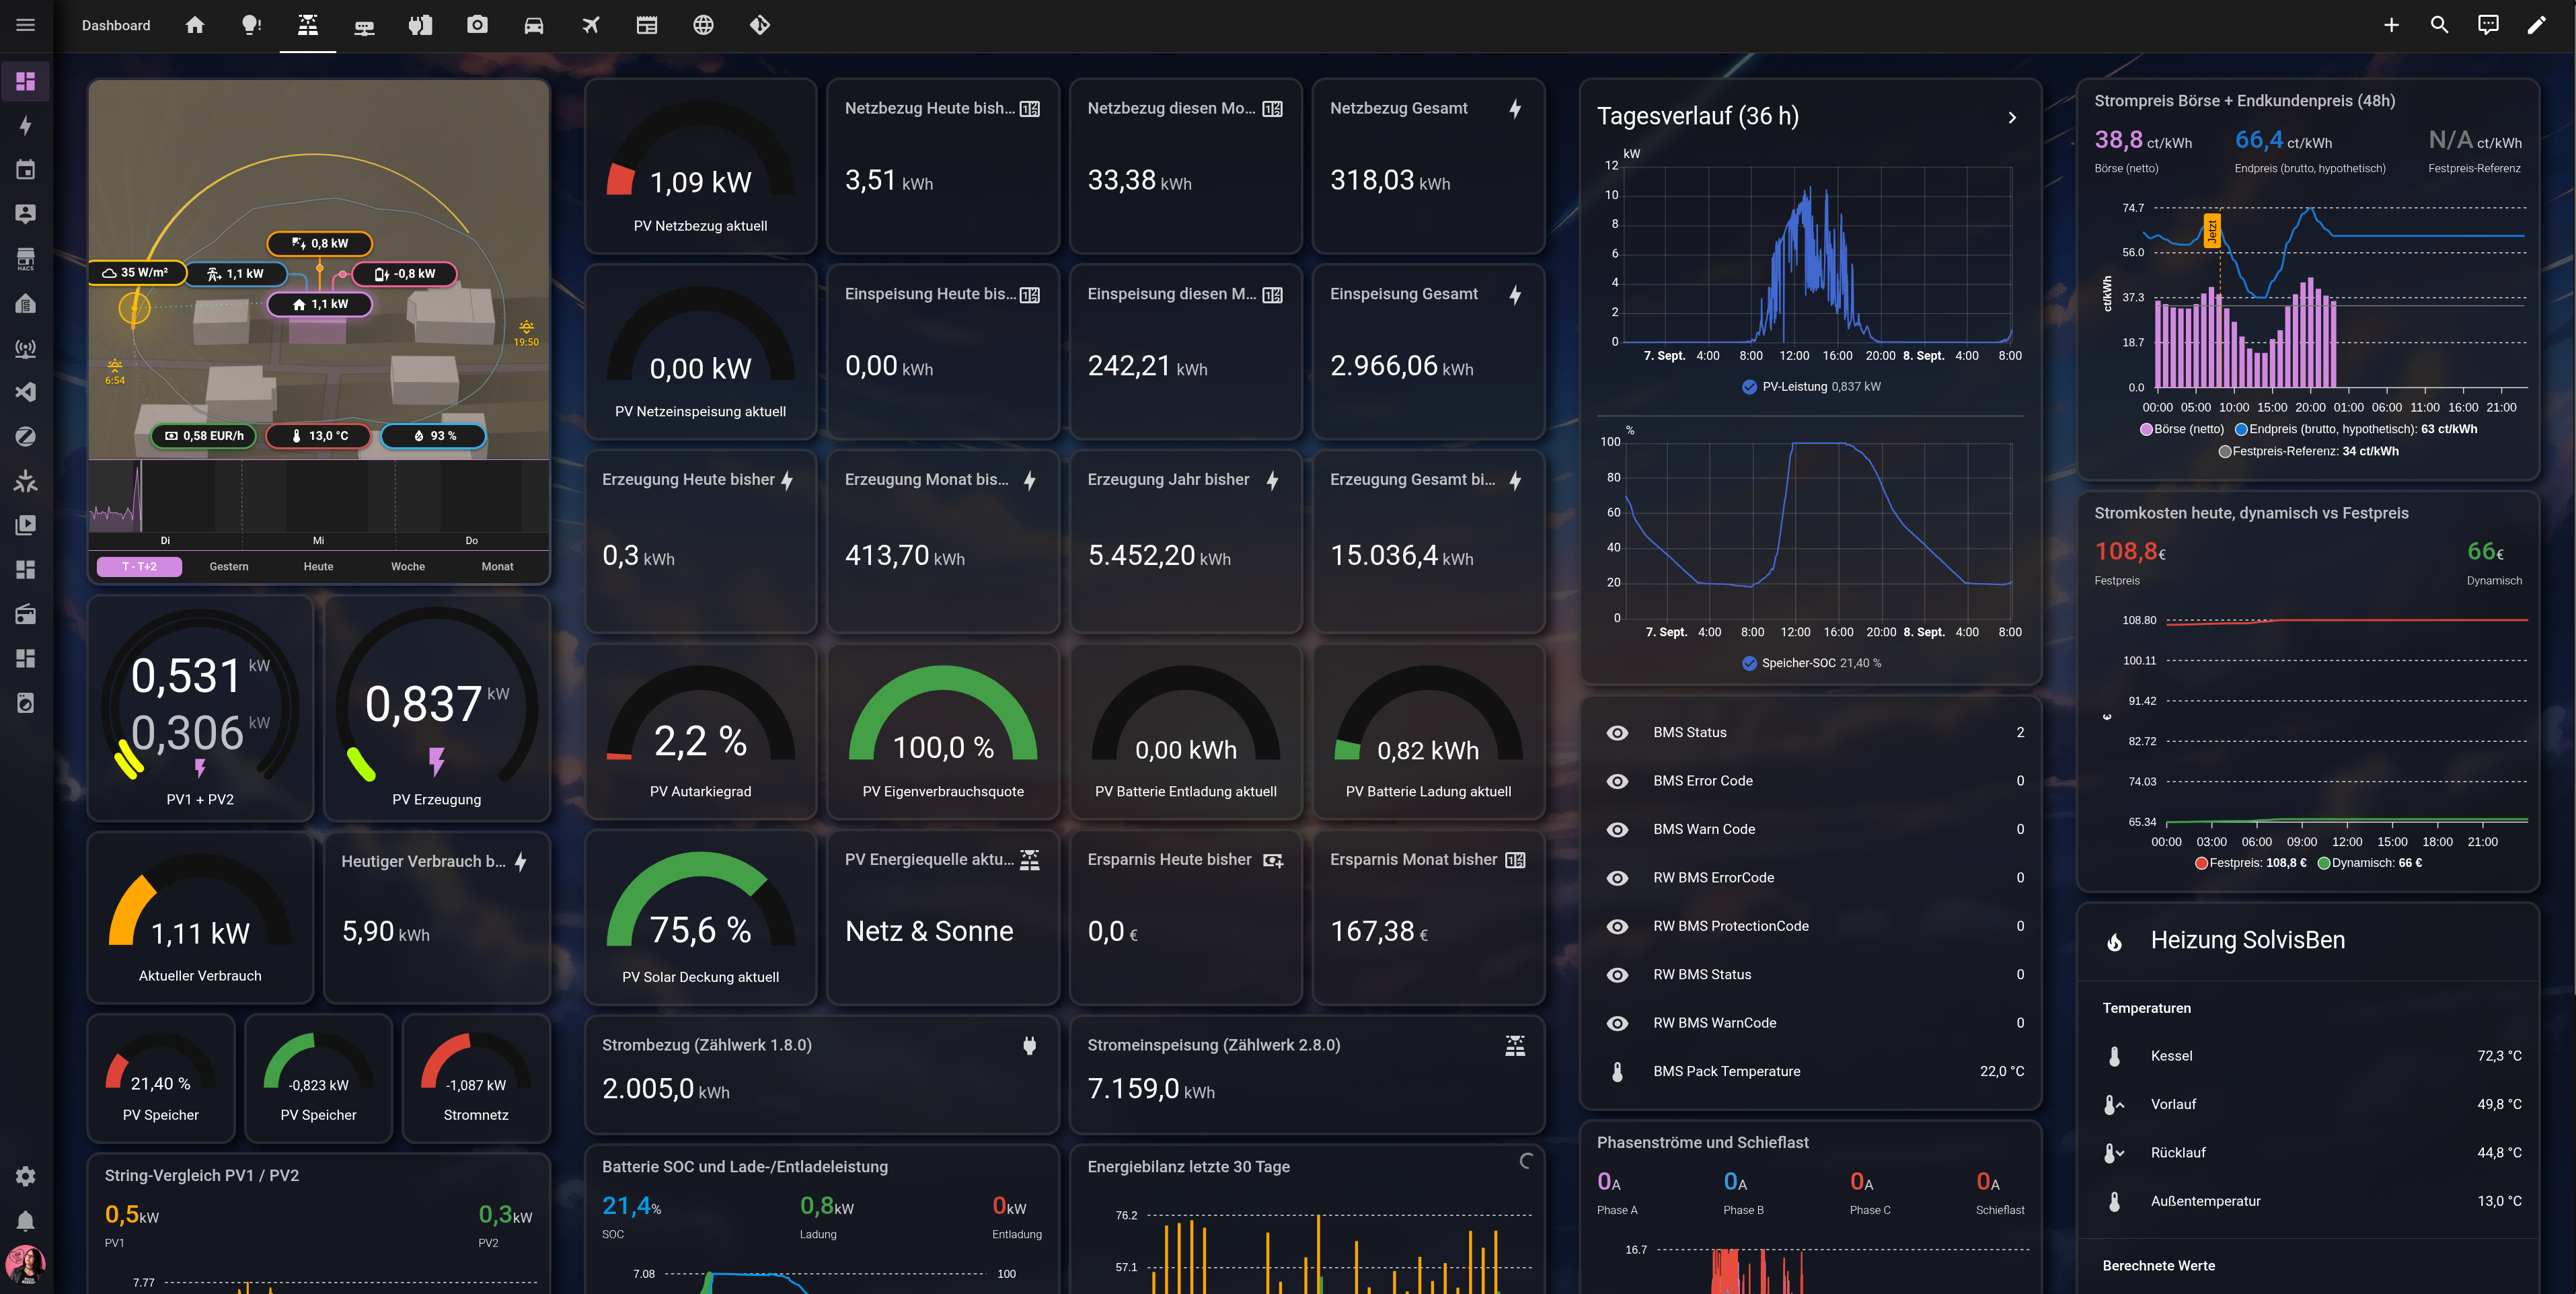
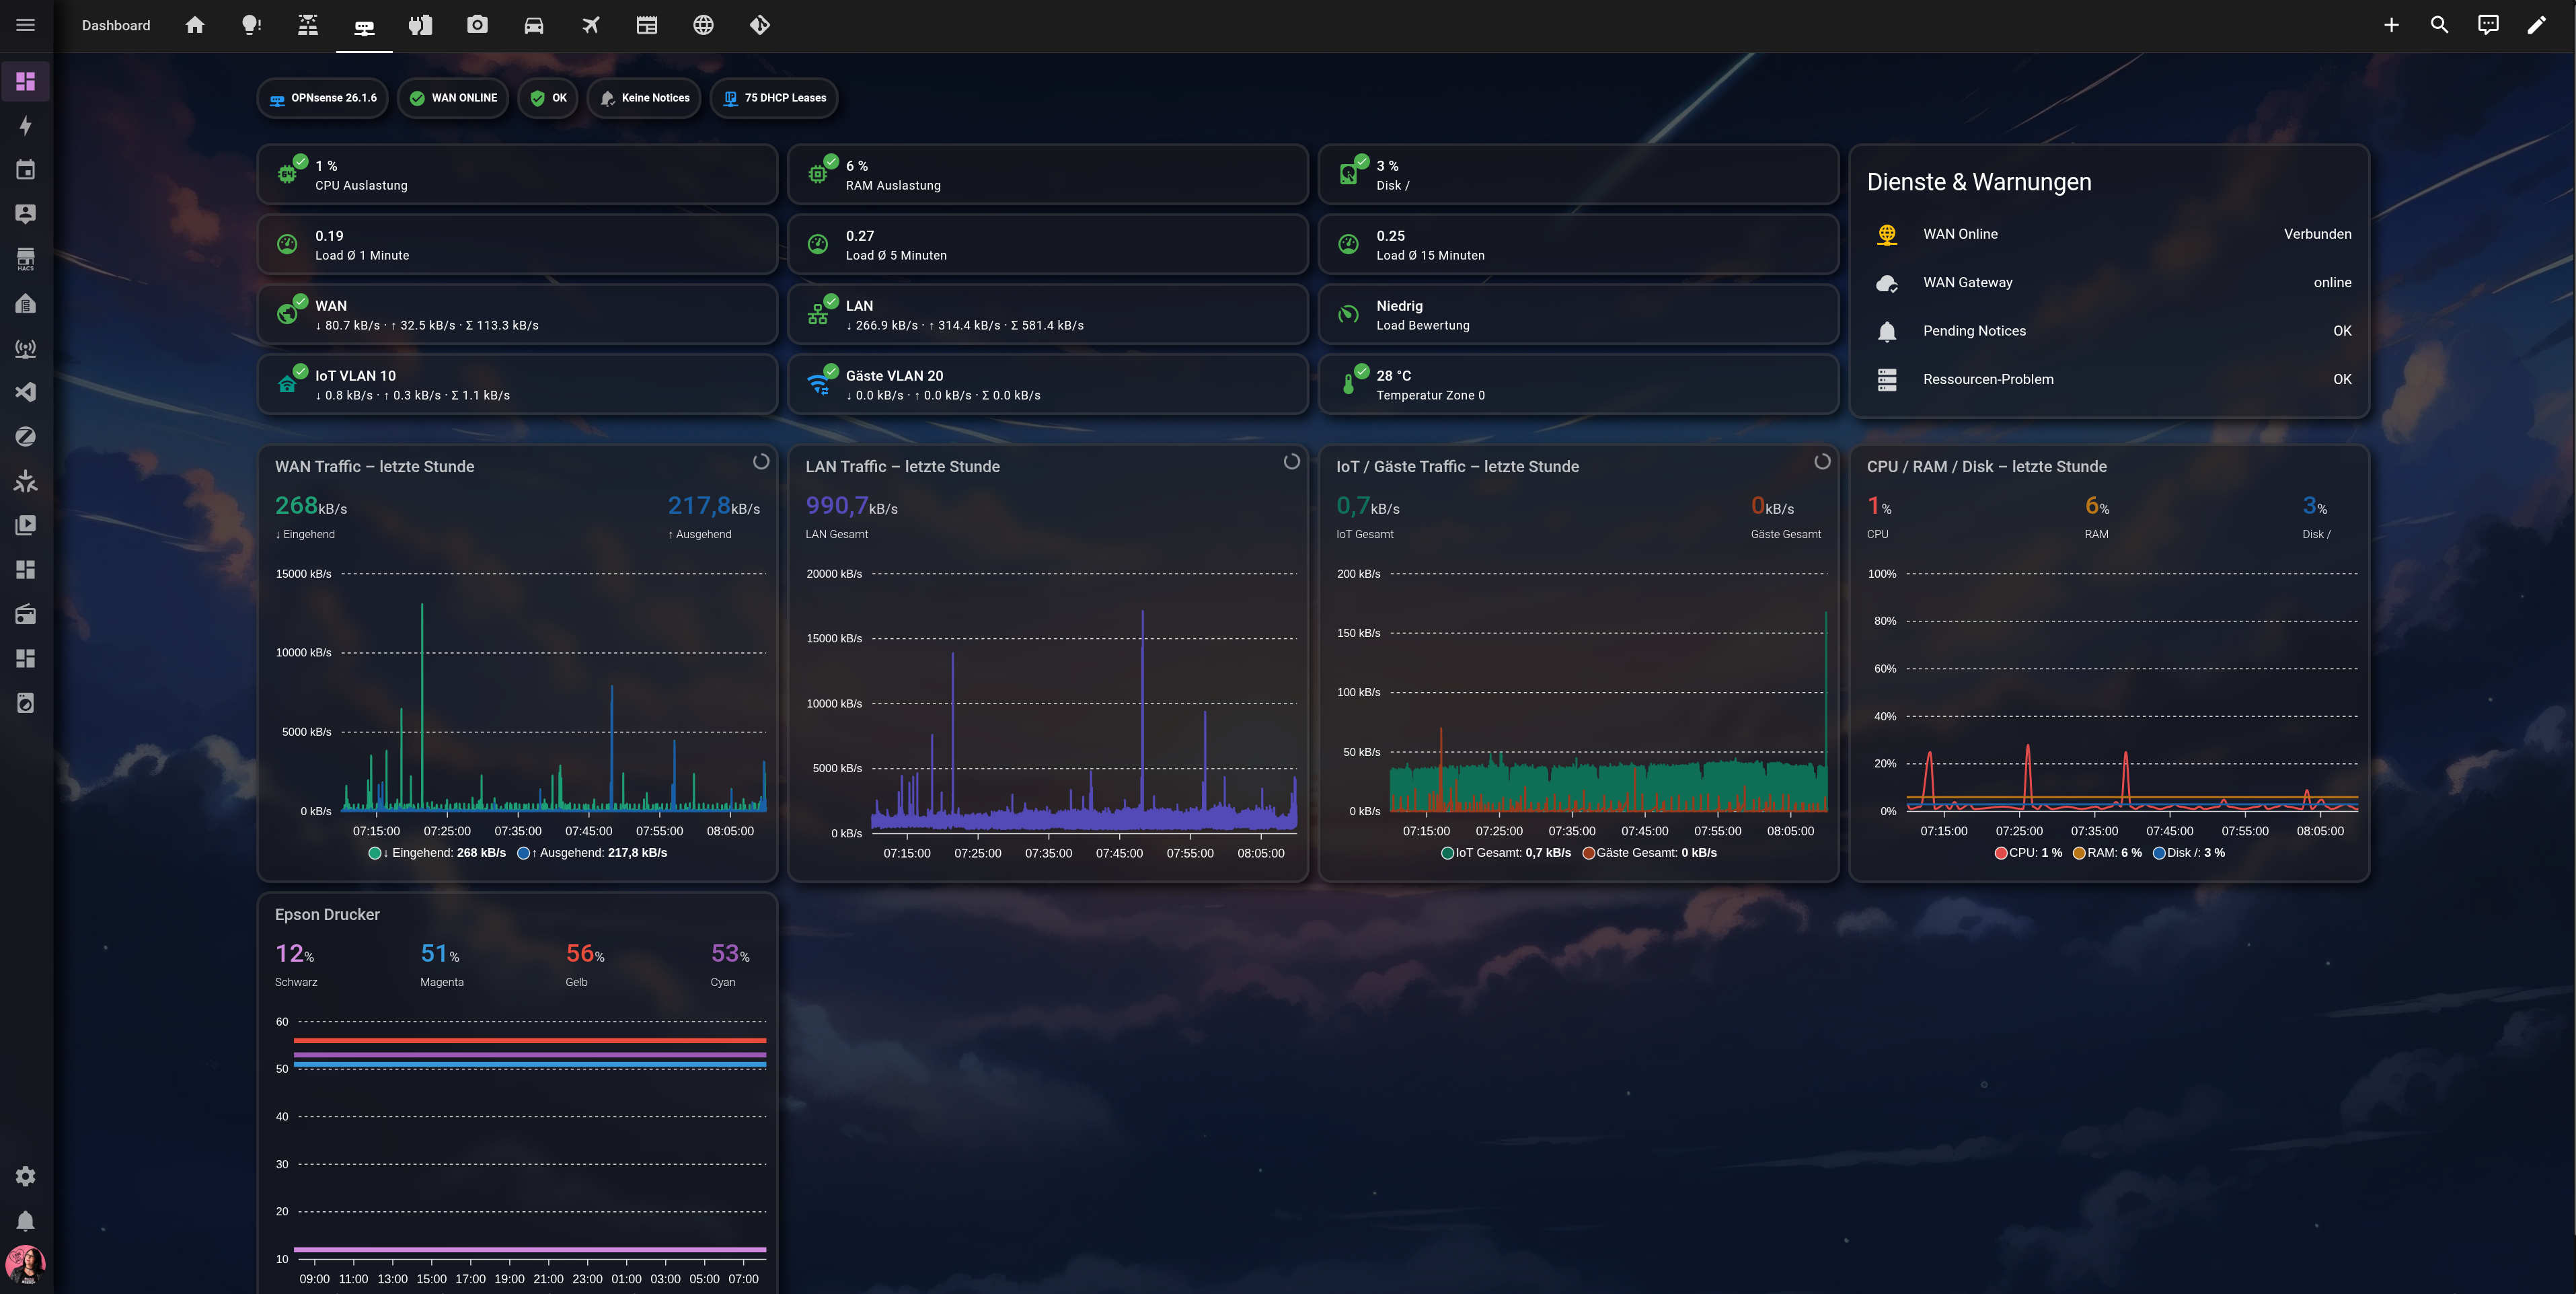
Ich hab mal mein Home Assistant Dashboard neu gebaut (erstes Bild). 😛 
Langsam gefällt es mir echt gut. Die ganzen anderen Seiten des Dashboards (Links oben in der Headbar) sind noch sehr Home Assistant Default. Aber eine kleine Auswahl hänge ich auch noch mit an.
Fragen erwünscht. :-P
#homeassistant #selfhosted #selfhosting #home #homeautomation #smarthome #dashboard
Fragen wir doch die KI. #mastodon #selfhosting

Alt...
Screenshot of a conversation about self-hosting a Mastodon instance with a custom URL. The dialogue includes a question about the possibility of running a personal Mastodon instance and a response confirming that it's possible, outlining the need to install and configure the Mastodon
Vor einigen Tagen bin ich über einen Toot von https://systemli.social/users/anneroth/statuses/117178159995091477 auf die Talos Reputation aufmerksam geworden und haben festgestellt das mein Blog (und einige andere Seiten die auf dem Server laufen) als "Malicious Site" eingestuft worden sind. Ich vermute das liegt an einer Portweiterleitung die dort eingestellt ist.
Ich habe einen Antrag (Button Submit Web Reputation Ticket) eingestellt und innerhalb eines Tages wurde die Einschätzung meiner IP auf "Neutral" geändert 🙂
Das soweit zur Qualität eine Dienstes wie Cisco Talos https://talosintelligence.com/reputation_center/
Well then…
After three years at Tailscale, today I’m starting a new chapter at Unraid as Head of Product Marketing.
I’m proud of what we built at #tailscale and enormously grateful to the people I worked with, and to everyone who watched the videos. 1600 subs to 78k, 10m views, and over 150 videos. Not too shabby.
Now I get to spend more time furthering the self-hosting mission I care so much about. I’ll be doing product work, community, technical education and, yes, plenty of video. There’s some really good stuff being worked on, and Unraid 8 will be a huge release.
At 10:15 I added a gently condescending toast for IPv4-only visitors. It called ipify, which felt inappropriate for someone running an ASN.
By 13:27 I had built a Rust/Axum IP service, put it behind Caddy, added MaxMind, three DNS names, trusted-proxy handling, an rc.d service, and a dedicated dual-stack FreeBSD VNET jail.
The toast looks exactly the same.
https://blog.hofstede.it/i-wanted-an-ipv4-toast-and-accidentally-built-an-ip-service/
It started as a gag: a tiny popup telling IPv4 visitors that their provider hasn't yet discovered 1998.
To do that honestly I needed something to echo the client address.
Using ipify felt wrong when you run your own AS. So now it's a service. 🙃
curl https://ip.hofstede.it
curl https://v6.ip.hofstede.it/json
curl https://v4.ip.hofstede.it/asn
One Rust binary, server-rendered, zero JavaScript.
The most real homelab tour you’ll see on YouTube this week! #selfhosting #homelab
Homelab Hardware Tour 2026 Edition
https://youtu.be/vktLEFH7t7c
🐡 Running your own mail server with OpenBSD and OpenSMTPD https://bsd-audit.com/self-hosting/running-your-own-mailserver/