Search results for tag #freebsd


EDIT: Please note, this post hasn't been update for a long time and still considers Dovecot 2.3.x - but the underlying ideas are still current.
Quite relevant, today:
Make your own E-Mail server - Part 1 - FreeBSD, OpenSMTPD, Rspamd and Dovecot included
Ich hatte eine rege Diskussion mit Microsoft Deutschland vor Ort an meinem Arbeitsplatz.
Man wollte mir erklären, dass #Opensource nicht skaliere. Ich habe so hart mit Ihm und seiner Kollegin diskutiert, mit einer ausführlichen Erklärung, dass er lüge und keine Ahnung hätte.
Dies führte vor 3 Wochen sogar zu einem Raunen in dem Raum seitens der Kollegen:innen der Standorte, welche vor Ort waren.
Ich sehe, wie es skaliert.
Lieblingssatz im Artikel von @heiseonline :
Microsoft sucht nach neuen Ansätzen, da „unsere Maßnahmen bislang nicht die erwartete Entspannung gebracht haben.“ Wie sich herausstellt, wird ein Kernprozss der Server überlastet, was zu deren Absturz und unzulänglichen Cloud-Kapazitäten führt…

The recording of the November 12th, 2026 #bhyve Production User Call is up:
We discussed several #FreeBSD fixes that help #Sylve, the vmm Test Harness, VM checkpoints, Sylve roles and delegation, Podman advantages, the Sylve GUI options, higher-performance storage for CI VMs, and more!
"Don't forget to slam those Bike and Describe buttons."
You can support all Call For Testing efforts via BSD Fund: https://bsdfund.org
This content is not AI generated

I've always appreciated the simplicity of the BSDs. Power, yes, but without unnecessary complexity.
BastilleBSD and vm-bhyve have been my trusted companions for many years. But whenever I used Linux, I missed them.
That's why, years ago, I started putting together a collection of shell scripts (and some Python, although to a much lesser extent) to create something somewhere in between.
A bit of Bastille, a bit of vm-bhyve, a bit of Proxmox: unprivileged Linux system containers and virtual machines, managed from the command line.
Live backups. And live restore: bringing a workload back online before all its data has finished copying from the backup. Multiple storage backends. Encryption at the storage or individual workload level. Different networks. Isolation of each workload (a bit like illumos zones), with additional layers of protection.
Each container has its own UID/GID mapping. VMs run under separate unprivileged identities, with namespaces, seccomp and resource limits adding further layers of protection.
Pull-based backups from external hosts, with different levels and types of encryption. With raw encrypted ZFS replication, the backup server doesn’t even need the decryption keys. Backups are pulled over SSH by an external server. The workload host holds no credentials to log in to that server.
It also runs on a 1 GB Orange Pi PC 2, where I’ve tested both containers and native ARM64 KVM guests. And on a Orange PI One, armv7 and 512MB, it can run some lxc containers without problems, from the SD, using f2fs.
Simple disaster recovery. Because after those 142 servers went up in flames in Strasbourg, disaster recovery became something I care a lot about.
Currently supported and tested on Alpine Linux, Debian 13 and Armbian. On Debian, LXC containers also run under enforcing AppArmor profiles, adding another layer of protection.
Few commands. Lots of power. And it's called "Jail It!"
I'm not going to release it, at least not for now. I need to focus on my other projects, and Jail It! still needs some cleaning up.
But it works. And it does its job very well.
For containers, there's absolutely nothing running in the background. For VMs, just a small Python helper. No continuously running services. You connect via SSH, run your commands, and that's it.
Still, for anyone curious enough to have a look, I've put together a short demo on Asciinema:
https://asciinema.org/a/BbwGs99U9UJDLAzZ
Well, "short" might be a bit of an exaggeration. It's quite long, but I think it's worth watching all the way to the end.
#Linux #LXC #KVM #FreeBSD #Virtualization #OwnYourData #BSD #SelfHosting #Homelab #SysAdmin #DisasterRecovery
I really, really reeaaallly want to see #Sylve becoming a FreeBSD based replacement or alternative to #Linux solutions like #XCPng (#Xen) or #Proxmox (#KVM).
Also interesting for my own @BoxyBSD@bsd.cafe project utilizing this feature. So, I've been working at this for some time now.
First working draft moving a VM which has its storage on a NFS server (ZFS based send/rec. as local storage to follow), including multi CPU support. But there's a catch - I'm not sure if I want to publish this later under MIT, rather than GPLv3 or AGPLv3, so this could be a problem for upstreaming.

Alt...
bhyve VM live migration on FreeBSD 15
Has anyone experimented with using a Linux jail for gaming? Would it work with Wine?
I have a game which has a launcher that would only run on Linux but it launches a game with Wine. I wonder if there's a way to run Wine on FreeBSD but keeps the launcher using linuxulator. 🤔
Missed the November 2026 FreeBSD Vendor Summit? You can now catch up on the presentations from both days on our YouTube channel!
We’re kicking off our video highlights with the first keynote from Day 1, “State of Cloud Native Computing on FreeBSD: OCI Containers, Kubernetes and LLMs,” presented by Carmi Weinzweig.
Watch the keynote: https://youtu.be/4ukp0E7kYP4
Be sure to check out our YouTube channel for individual presentations from both days of the Summit.


FreeBSD Developer AI survey
https://www.freebsd.org/status/report-2026-07-2026-09/#_freebsd_core_team
Alt...
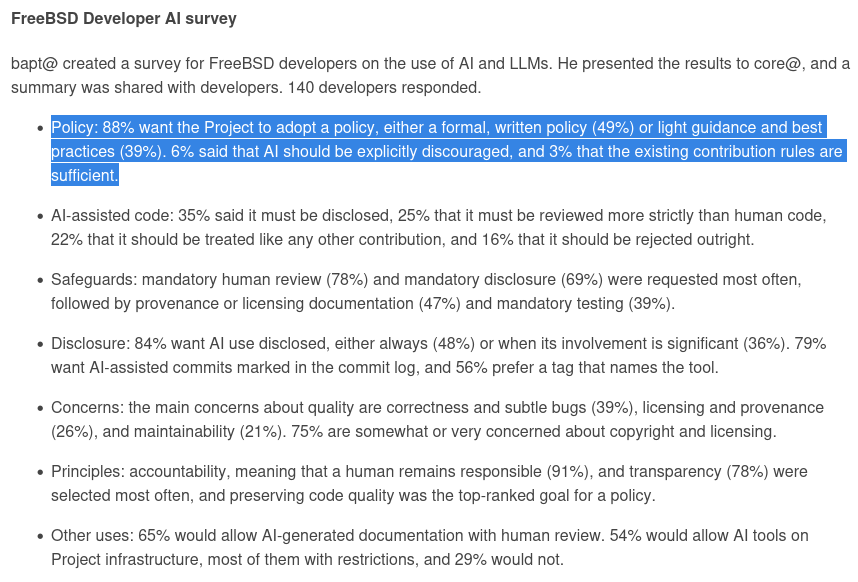
FreeBSD Developer AI survey
bapt@ created a survey for FreeBSD developers on the use of AI and LLMs. He presented the results to core@, and a summary was shared with developers. 140 developers responded.
Policy: 88% want the Project to adopt a policy, either a formal, written policy (49%) or light guidance and best practices (39%). 6% said that AI should be explicitly discouraged, and 3% that the existing contribution rules are sufficient.
AI-assisted code: 35% said it must be disclosed, 25% that it must be reviewed more strictly than human code, 22% that it should be treated like any other contribution, and 16% that it should be rejected outright.
Safeguards: mandatory human review (78%) and mandatory disclosure (69%) were requested most often, followed by provenance or licensing documentation (47%) and mandatory testing (39%).
Disclosure: 84% want AI use disclosed, either always (48%) or when its involvement is significant (36%). 79% want AI-assisted commits marked in the commit log, and 56% prefer a tag that names the tool.
Concerns: the main concerns about quality are correctness and subtle bugs (39%), licensing and provenance (26%), and maintainability (21%). 75% are somewhat or very concerned about copyright and licensing.
Principles: accountability, meaning that a human remains responsible (91%), and transparency (78%) were selected most often, and preserving code quality was the top-ranked goal for a policy.
Other uses: 65% would allow AI-generated documentation with human review. 54% would allow AI tools on Project infrastructure, most of them with restrictions, and 29% would not.

The new versions of openpgp-card-tools-git (0.1.9) and openpgp-card-ssh-agent (0.3.8) with the new Ephemeral PIN backend are now in the FreeBSD ports tree, and packages will show up in the "latest" branch in 2-4 days. 
Tested with a real card on FreeBSD 15.1: works great!
https://www.freshports.org/security/openpgp-card-tools-git/
https://www.freshports.org/security/openpgp-card-ssh-agent/


BSD folks: Is there a native #FreeBSD, #OpenBSD, or #NetBSD tool for managing system-wide trust-anchors? Debian has something like
$ sudo dpkg-reconfigure ca-certificates
which gives an interactive TUI allowing me to specify which CAs I do/don't trust, and they get picked up system-wide.
Ideally this would persist past most package/system upgrades too so I don't have to (re)do it every time ca-certificates gets updated from repos.

🚀 Waterfox 6.7.8 has been updated in FreeBSD Ports.
The latest Waterfox release is now available for FreeBSD through the Ports Collection.

I think more people should know about #reflinks, which I learned about from @leah years ago.
(100% human-written prose. I use em dashes and bulleted lists because they make the prose clearer. Also, I like them.)
Immutable copy-on-write snapshots of things are kind of a superpower for computer systems design. (FP folks call this "persistence.") An awfully large fraction of computers' time is spent copying things from one place to another to keep them from changing. In a lot of cases, this is unnecessary, because they weren't actually going to change in the first place, but it can be hard to be sure in advance. If you have some kind of system that will copy *only* the things that get modified — or the *parts* of those things that get modified — it will often be much more efficient. So, in Linux, we use this a lot in copy-on-write memory mappings of files, process memory following a fork(), and things like that. rsync has a --link-dest option that allows multiple backups to share space while being just as convenient to use as regular non-incremental backups. There are many other examples.
Some OSes and some filesystems support making a copy-on-write "copy" of a file, sharing the space between the original file and the "copy" until and unless one of them change. This feature is usually called "reflinks" after the Solaris system call that supports it.
In particular:
On #Linux:
- Bcachefs,
- btrfs,
- XFS, and
- OCFS2.
But *not* OpenZFS.
On #FreeBSD, neither OpenZFS nor #ZFS.
On Solaris, ZFS (with `cp -z`).
On MacOS, APFS (which Apple is switching to; with `cp -c` or the `clonefile` system call)
And, on Microsoft Windows, NTFS and its DUPLICATE_EXTENTS_TO_FILE.
These are from Daniel Aleksandersen's 02020 blog post https://www.ctrl.blog/entry/file-cloning/. I don't think anything has changed on that front since then, which is sad, if true.

Was chatting with Hayzam yesterday about Sylve and integrating daemonless (https://daemonless.io) directly into it. Seeing it turn painful setups like Grafana and VictoriaMetrics into 10-second deployments is exactly why we're doing this.
It hit on a familiar feeling: remember when getting a new phone was exciting? Setting up every app, tweaking configs, logging into everything. Nowadays, it's just a chore you want over with. Babysitting packages and doing low-level sysadmin work on standalone jails feels the exact same way.
Wrote down some thoughts on moving past that friction: https://ahze.net/posts/the-new-phone-feeling/
#FreeBSD #daemonless #Sylve #containers #SelfHosted #SysAdmin
Latest 𝗩𝗮𝗹𝘂𝗮𝗯𝗹𝗲 𝗡𝗲𝘄𝘀 - 𝟮𝟬𝟮𝟲/𝟭𝟭/𝟬𝟵 (Valuable News - 2026/11/09) available.
https://vermaden.wordpress.com/2026/11/09/valuable-news-2026-11-09/
Past releases: https://vermaden.wordpress.com/news/
#verblog #vernews #news #bsd #freebsd #openbsd #netbsd #linux #unix #zfs #opnsense #ghostbsd #solaris #vermadenday
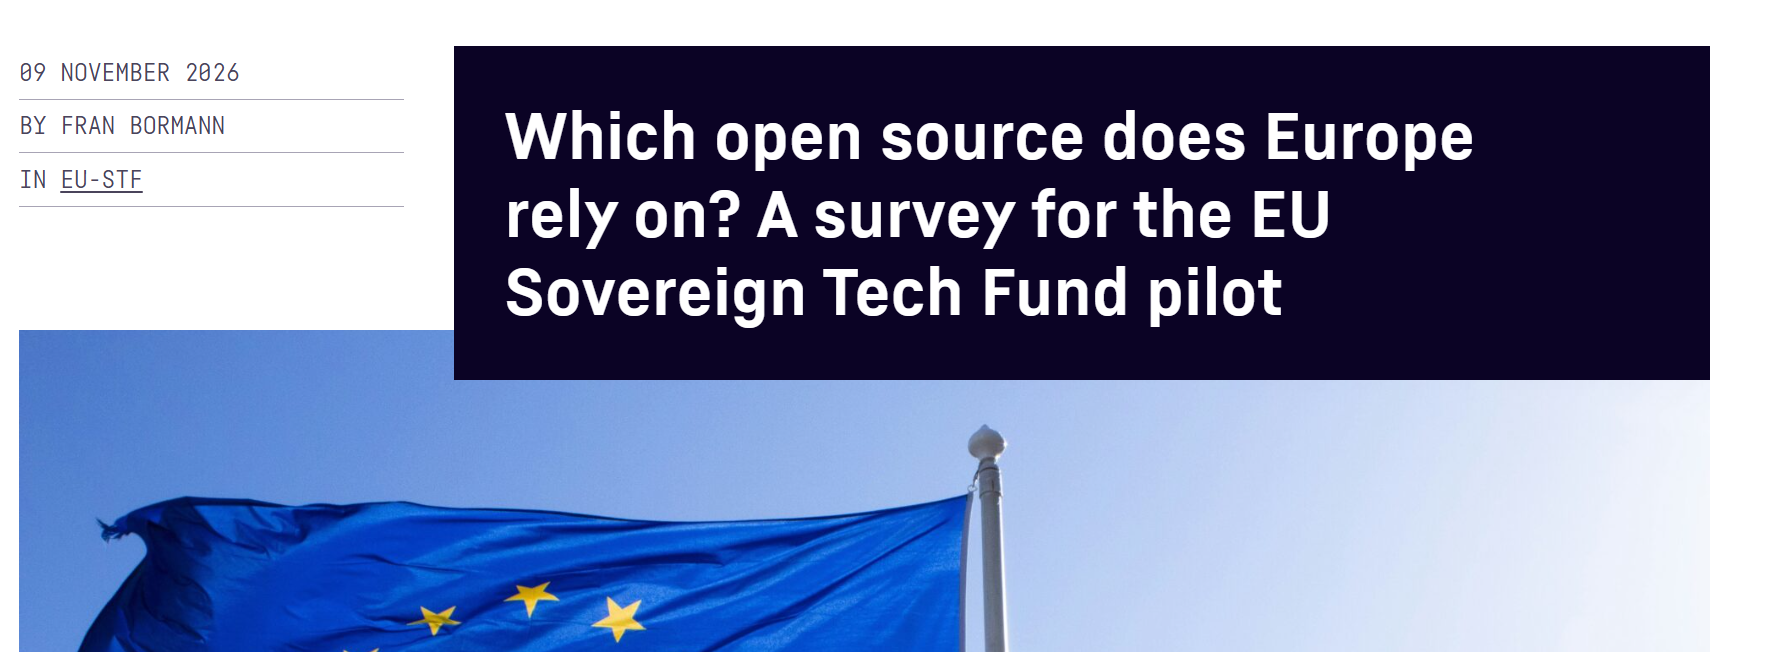
The Sovereign Tech Agency is seeking input from the open source community to help shape the EU Sovereign Tech Fund pilot, an initiative focused on supporting critical open source technologies that Europe's digital infrastructure depends on.
We encourage FreeBSD users and contributors, particularly those in Europe, to participate and share their perspectives on the open source infrastructure they rely on.
Take the survey: https://survey.sovereign.tech/eustf
#FreeBSD #OpenSource #EUSovereignTechFund
Manpage Monday: bastille config
Get, set, add or remove jail properties — no manual jail.conf edits.
Allow mlock inside a jail
> bastille config myjail set allow.mlock 1
Set a start priority
> bastille config myjail set priority 10
Read a value back
> bastille config myjail get boot
See `man bastille-config` for more details.
For the past six years, I’ve kept a quarterly ritual of donating to a free and open-source software project that recently helped me in my life or work.
Here is my 2026 lineup. With a special exception for Q4:
• Q1: FreeBSD Foundation (@FreeBSDFoundation)
• Q2: KeePassXC (@keepassxc)
• Q3: KDE e.V. (@kde)
• Q4: Sanktionsfrei e.V. (@Sanktionsfrei)
Not a FOSS project, but more important. Standing together for fear-free, dignified basic income support without sanctions in Germany! 🤝❤️
#FOSS #OpenSource #FreeBSD #KeePassXC #KDE #Sanktionsfrei #Bürgergeld #Solidarität #Fediverse


portscout integration with FreshPorts - now (on dev and test) you see the upstream version, if newer, on the port page.
https://news.freshports.org/2026/11/08/upstream-versions-on-the-port-page/
e.g. https://test.freshports.org/accessibility/at-spi2-core/
Haven't tried OCI containers on FreeBSD yet? Try fjord, a web UI app store for FreeBSD containers.
6-minute walkthrough: https://youtu.be/8S3hEVyCUzc
Not your thing? Sylve (nightly) and FreeCORE run daemonless images too, and so does plain Podman or AppJail.

Typical example of the sort of myopia that is usually part of using the generic "BSD" moniker:
https://docs.ansible.com/projects/ansible/latest/os_guide/intro_bsd.html says "how to use this on BSD"; it has examples for both BSDs -- #FreeBSD and #OpenBSD and does not mention #NetBSD a single time!
I keep seeing this. Why?
Day 2 of the 2026 FreeBSD Vendor Summit kicks off today at NetApp's headquarters in San Jose, California.
You can follow the sessions live here:
https://www.youtube.com/watch?v=cnkmRe4nsOU
This week, I had to do some work with Linux, so I found myself working with Alpine Linux again. And, of course, one of the worst and most absurd security vulnerabilities in recent times popped up. 😆
Fortunately, none of my setups met the conditions required for exploitation.
That said, I've been running some interesting experiments on a Raspberry Pi 4, the same one that has been running FreeBSD for quite some years, hosting a Time Machine service in a jail and handling backups from other servers.
Long story short, I installed Alpine Linux on the Raspberry Pi and moved FreeBSD into a KVM virtual machine, with the disks passed through directly to it.
The result? The VM runs beautifully with 3 GB of RAM (possibly even 2 GB), and I still have the rest of the Raspberry Pi available to run OpenBSD, NetBSD, and other systems I need for different setups.
It's a sad that bhyve doesn't (yet) support virtualization on that device. Or at least, that was still the case the last time I checked.
burningboard.net is now running Mastodon 5.0.0-beta.1! 
The upgrade from 4.7.5 went surprisingly smoothly on FreeBSD 15.1 with Bastille jails. The biggest hurdle was Ruby: 5.0 requires exactly 4.0.9, and the FreeBSD package isn’t there yet. So: Ruby 4.0.9 via rbenv first, then the Mastodon upgrade.
New highlights include the redesigned web interface and colour themes. Since this is a beta, please let me know if anything looks off.
burningboard.net läuft jetzt auf Mastodon 5.0.0-beta.1!
Das Upgrade von 4.7.5 lief auf FreeBSD 15.1 in Bastille-Jails erstaunlich glatt. Der größte Brocken war Ruby: 5.0 verlangt exakt 4.0.9, das FreeBSD-Paket ist noch nicht so weit. Also erst Ruby per rbenv auf 4.0.9, dann das Mastodon-Upgrade.
Neu sind unter anderem das überarbeitete Webinterface und die Farbthemen. Da es eine Beta ist, meldet euch bitte, falls euch etwas auffällt.
Three Rust tools, one hardware key, no GnuPG in the path.
I ported oct, oct-git and openpgp-card-ssh-agent from the OpenPGP Card project to FreeBSD, and all three are now in the ports tree. openpgp-card-tools is already in pkg latest, the other two follow soon.
The article covers what each tool does, how they share PIN handling, and my setup on Fedora and on my FreeBSD T480.
The 2026 FreeBSD Vendor Summit begins today at NetApp Headquarters in San Jose, CA.
The FreeBSD Foundation is excited to welcome the community to the 2026 FreeBSD Vendor Summit, taking place November 5–6, 2026.
You can follow the sessions live here:
https://www.youtube.com/watch?v=EuCJrgphP8c
We’ll share Day 2 highlights in a separate update.
#FreeBSD #VendorSummit #OpenSource
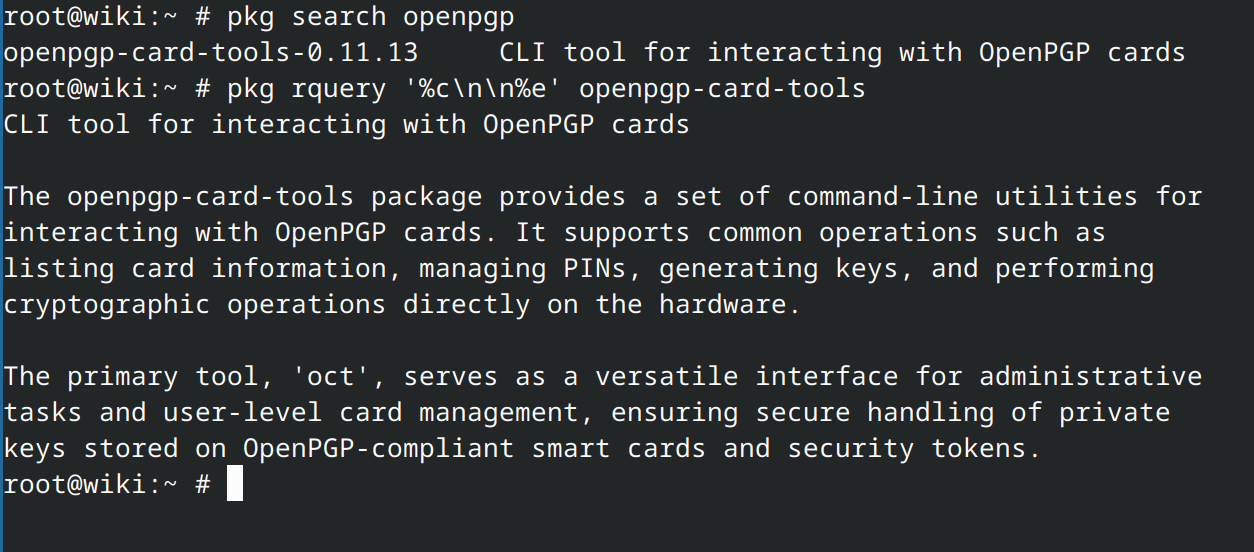
The OpenPGP card stack is now complete on FreeBSD! Joining oct, openpgp-card-ssh-agent and openpgp-card-tools-git just landed in ports:
oct: manage YubiKeys, Nitrokeys & co. from the CLI
https://www.freshports.org/security/openpgp-card-tools/
openpgp-card-ssh-agent: SSH login with the key on your card, works with standard clients
https://www.freshports.org/security/openpgp-card-ssh-agent/
oct-git: hardware-backed Git signing and verification
https://www.freshports.org/security/openpgp-card-tools-git/
Private keys never leave the card. 😃
Thanks to Heiko Schaefer ( @hko ) & ( @wiktor ) for the tools and Älven for the commits!
#FreeBSD #OpenPGP #Security #PGP #RunBSD #Cryprography //cc @feld
Finally, openpgp-card-tools from @hko landed in the FreeBSD package repositories.
Upstream-Project: https://codeberg.org/openpgp-card/openpgp-card-tools
FreeBSD Port: https://www.freshports.org/security/openpgp-card-tools/
It's a command-line utility to manage OpenPGP Cards and compatible devices (Yubikey, Nitrokey, etc). More tools from the same ecosystem (oct-git, ssh-agent) are in the works for FreeBSD 🙂
#freebsd #pgp #cryptography #opensource
This looks interesting, especially if your hosts are not where your package repo is.
git-proxy is a caching proxy for package registries. It sits between package managers and their upstream repositories, keeps a local copy of every package it serves, and keeps serving them while the upstream is unreachable.
My use case: Updating pkg-base jails. After the first install / pkg-update, the packages are local.

WorldMonitor is now available for FreeBSD.
WorldMonitor is an open source dashboard for real-time global intelligence. It brings news, markets, commodities, energy, supply chains, conflicts, military activity, natural disasters and risk indicators together on one map and in one set of panels. It aggregates many public data sources and is aimed at anyone who wants a single view of what is happening in the world.
On FreeBSD it runs self-hosted in the browser: pkg install worldmonitor, start the services, open the dashboard. A separate client brings the same data to the terminal.
Some panels need API keys for their data sources, and the Pro features and sign-in depend on the WorldMonitor service. The package documentation explains what is needed.
The pages on portstatus:
https://portstatus.bsdproject.de/www/worldmonitor/
https://portstatus.bsdproject.de/www/worldmonitor-cli/
The November 3rd, 2026 Jail/Zones Production User Call is up:
We discussed OCI container/#bhyve integration, a CPU caching surprise, #Sylve/Daemonless integration, Sylve/TrueNAS comparisons, secrets management in container environments, moving from s6rc to #FreeBSD rcd(8), and more!
"Don't forget to slam those Like and Subscribe buttons."
You can support all Call For Testing efforts via BSD Fund: https://bsdfund.org
This content is not AI generated
https://portstatus.bsdproject.de now writes VuXML entries for you. Tick the unaddressed CVEs on a port page and you get a ready entry: the package names the port really builds, ranges in pkg notation with epoch and revision, one range per epoch the port had, every bound checked with libpkg.
The limit is CPE. Only 3,331 of 34,927 ports carry one, the rest never get matched. Ports sharing a CPE can get a version that never existed for them, so check before you commit.
Manpage Monday: bastille tags
Organize your jails with labels.
Tag two jails as prod at once
> bastille tags 'myjail yourjail' add prod
List every jail carrying the web tag
> bastille tags ALL list web
Tags make it easy to target groups of jails across your fleet.
> bastille service TAG nginx restart
> bastille sysrc TAG -ae
See `man bastille-tags` for more details.
Latest 𝗩𝗮𝗹𝘂𝗮𝗯𝗹𝗲 𝗡𝗲𝘄𝘀 - 𝟮𝟬𝟮𝟲/𝟭𝟭/𝟬𝟮 (Valuable News - 2026/11/02) available.
https://vermaden.wordpress.com/2026/11/02/valuable-news-2026-11-02/
Past releases: https://vermaden.wordpress.com/news/
#verblog #vernews #news #bsd #freebsd #openbsd #netbsd #linux #unix #zfs #opnsense #ghostbsd #solaris #vermadenday

Yet NetBSD still really appeals to me, Reminding me of the good old days and it even provides excitement in trying to get things going all from the CLI. 🤔😍

Monthly reminder to periodically check your bastille.conf for updates or new entries from the sample config:
cd /usr/local/etc/bastille
diff -u bastille.conf bastille.conf.sample
We try to keep config updates to a minimum, but sometimes they are required.