Search results for tag #ansible
ansible-jailexec 2.0.4 is out 🎉
jailexec is an Ansible connection plugin that runs tasks in FreeBSD jails via jexec on the jail host, no sshd inside the jails needed.
Bugfix: with delegate_to between jails, tasks silently ran in the original host's jail, because Ansible keeps inventory_hostname pointing at the original host and jailexec used it as the jail name.
If you delegate between jails, upgrade and check what earlier runs changed.
Thanks to the user who reported it privately with a perfect reproducer!
https://github.com/chofstede/ansible_jailexec/releases/tag/v2.0.4
@rainer
#gitlab #ansible upgrade
Grüße
gitlab_upgrade.yml:
---
- name: GitLab Update Playbook
hosts: all
become: yes
tasks:
- name: Setze GitLab-CE auf unhold
ansible.builtin.dpkg_selections:
name: gitlab-ce
selection: install
- name: Backup von GitLab erstellen
command: gitlab-backup create
- name: Führe ein apt upgrade für GitLab durch
apt:
name: gitlab-ce
state: latest
- name: Blockiere das Update für GitLab-CE
ansible.builtin.dpkg_selections:
name: gitlab-ce
selection: hold%
 boosted

Wir haben noch eine Stelle zu besetzen: Als System-Administrator:in (Linux, Ansible) für unsere SaaS-Plattform @pretix sowie zahlreiche interne Tools in unserem Ops-Team mit großartigen Kollegen. 30-40h/W, fully remote (in .de), bunte Mischung aus Tagesgeschäft und Projekten, strukturiertes Gehaltsmodell mit Minimum bei 4.895 € brutto plus Benefits.
Alle Infos:
https://pretix.eu/about/de/job/ops
#fedihired #fedijobs #remotejobs #linux #ansible #fedihire #getfedihired #sysadmin
How to annoy two purist camps at once:
1. Run FreeBSD 15.1-RELEASE on a ThinkPad T480.
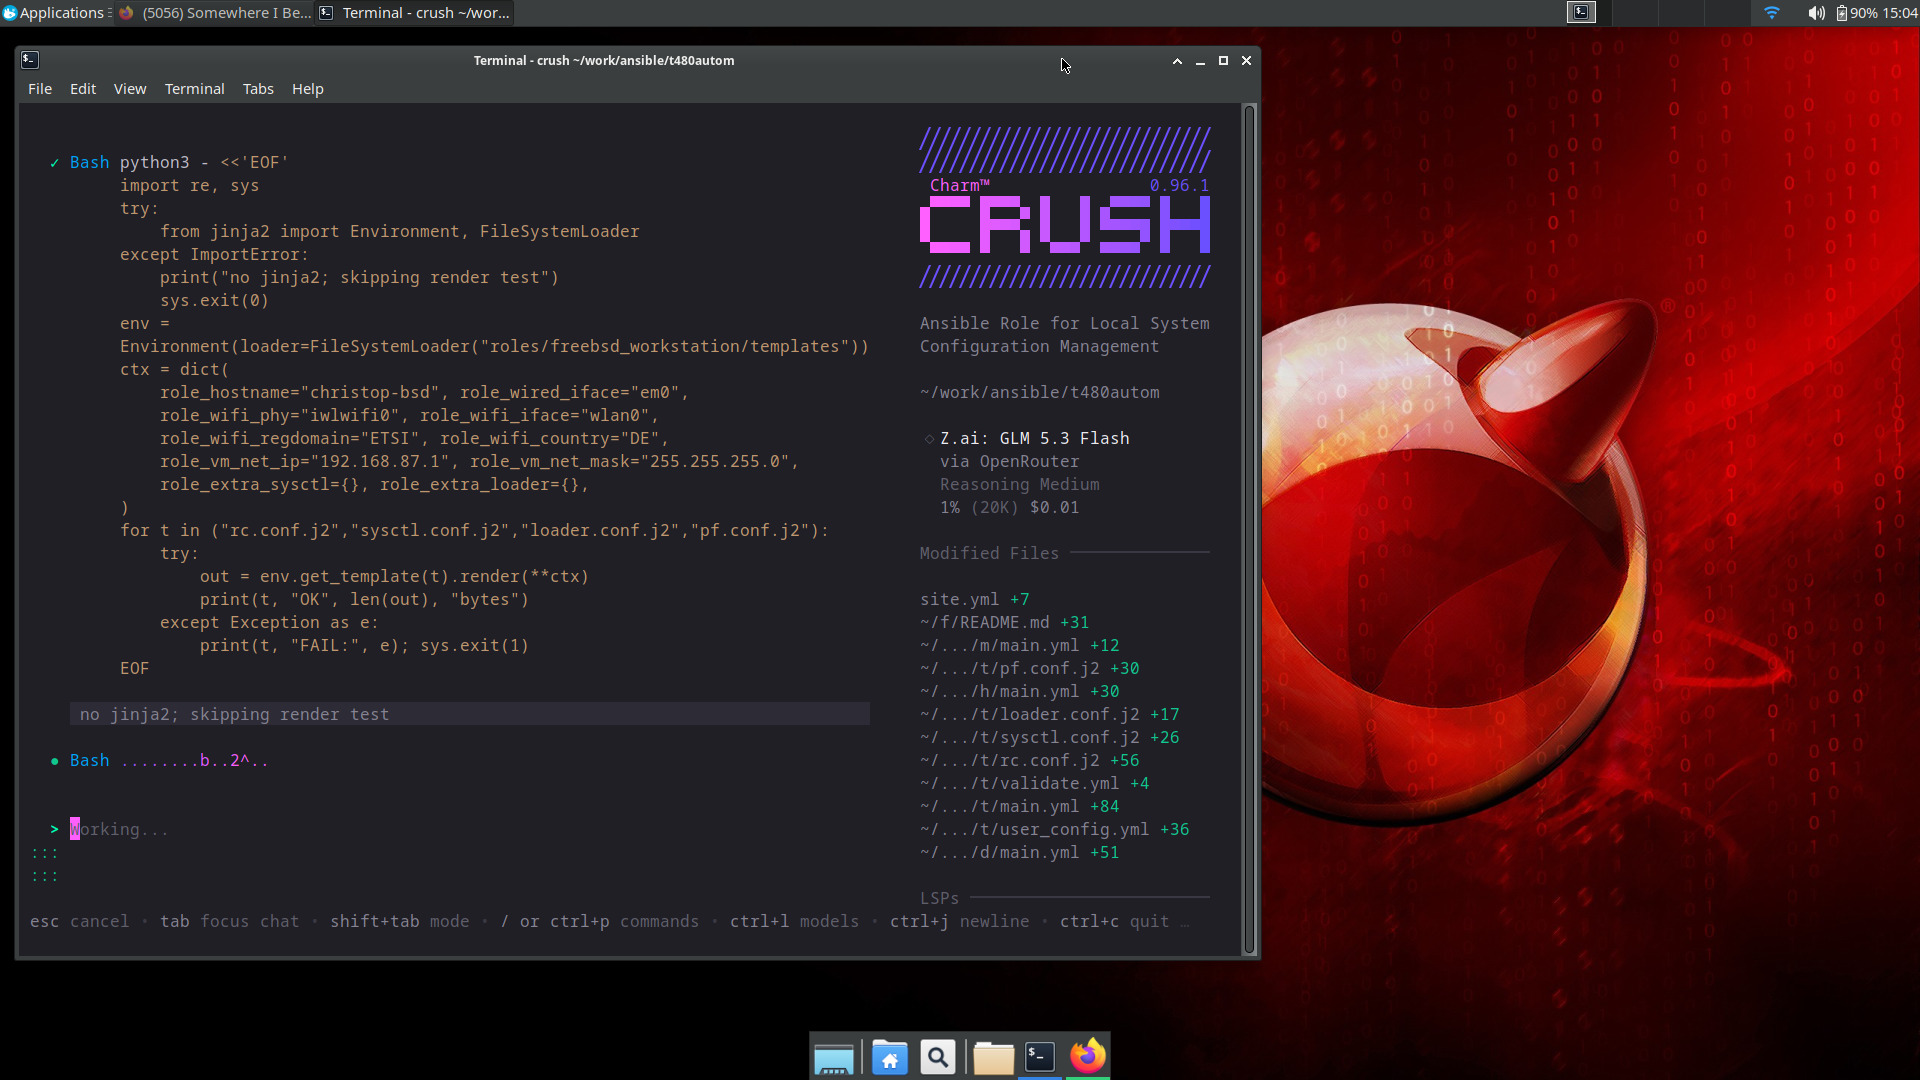
2. Let an agentic AI (Crush + GLM 5.3 Flash) write the Ansible roles for rc.conf, pf.conf, and loader.conf.
I know AI isn't the most popular topic around here, but watching a TUI agent haggle with a missing Jinja2 module in real time is great entertainment for a single cent. And the result was actually good after reviewing and tweaking it just a little.
#FreeBSD #RunBSD #ThinkPad #T480 #Ansible #DevOps #bsdcafe #ai #genai
Alt...
A desktop screenshot of a FreeBSD system featuring the red Beastie daemon wallpaper. An open terminal window runs the Charm Crush CLI agent (v0.96.1) inside the directory ~/work/ansible/t480autom. The right pane displays the Crush logo, context info showing the model "Z.ai: GLM 5.3 Flash via OpenRouter", and a list of modified Ansible and template files including site.yml, rc.conf.j2, sysctl.conf.j2, pf.conf.j2, and loader.conf.j2. The left pane shows an automated bash execution running an inline Python test using Jinja2 to render configuration templates with network parameters for host 'christop-bsd'.
I write Ansible for a living. Until recently I still patched most of my own servers by hand, one SSH session at a time.
Now: freebsd-update and pkgbase, thin Bastille jails, thick jails via jailexec, a Proxmox cluster, RHEL. Dry runs first, explicit reboot policies, and an honest list of what still isn't covered.
Plus the reboot I should have seen coming.
The Ansible guy finally uses Ansible on his own infra 🙈
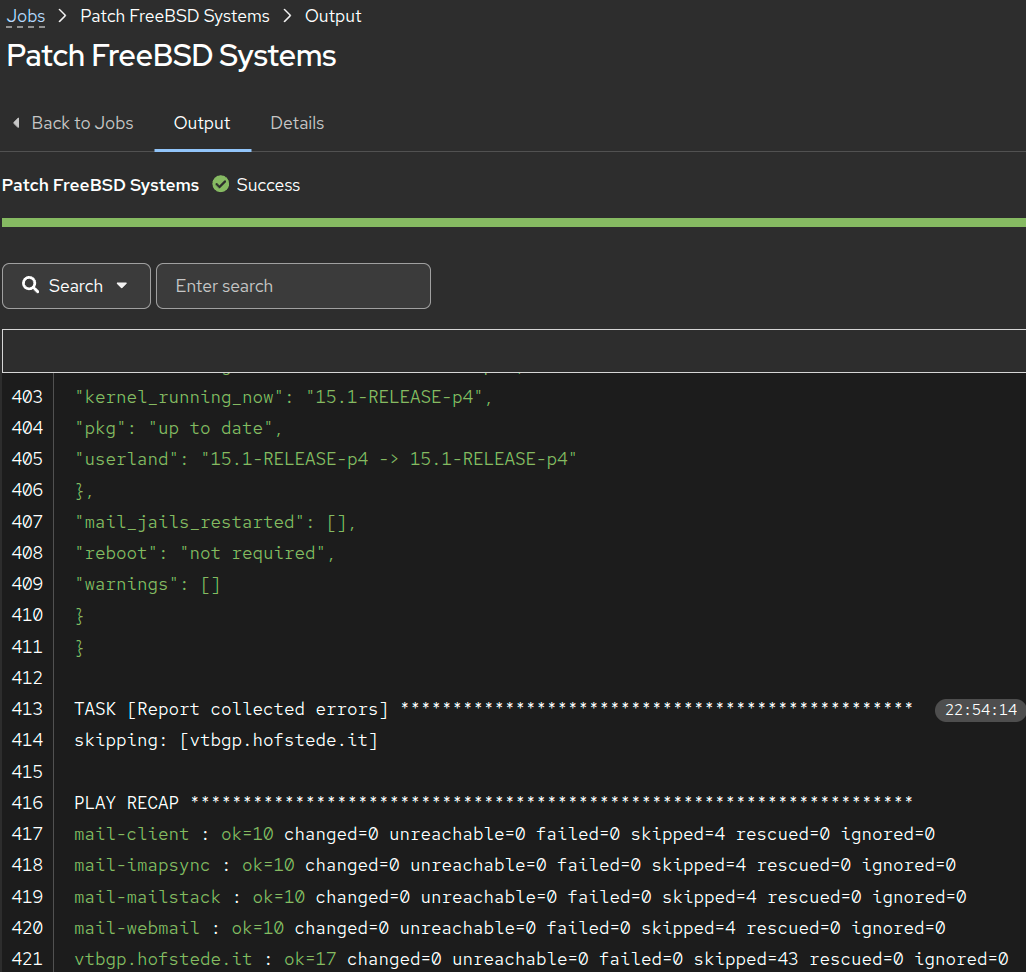
Today FreeBSD routers, Bastille jail hosts, the mail server and the Proxmox cluster + PBS moved to AAP: git inventory, defensive patch playbooks, and a curated Private Automation Hub as the only collection source.
Jails are patched via my jailexec connection plugin, now also a collection. Already on GitHub, Codeberg & PyPI - Ansible Galaxy release coming soon!
https://github.com/chofstede/ansible_jailexec/
#Ansible #FreeBSD #AAP #Proxmox


v2.4.0 of my ansible-jails module is now available:
https://git.sr.ht/~dch/ansible-jails
In particular, it supports base system packaged jail templates, and will use them by default on FreeBSD 15+ systems, and improved corner cases for 14.x and 16.0-CURRENT, as well.
Thanks to @beni I fixed a number of IPv6 related bugs, and no-IP jails bugs too.
It has a significant improvement in test coverage thanks to Ansible Molecule, and https://sourcehut.org/ CI, so we know that both post-jail templates & ZFS usage works as expected!
v3.0.0 might come out this week, with VNET jail support. I don't expect this to be a significant change, it's just that I personally never tested it, and it seems like a good milestone.
ansible-jailexec 2.0.3 is out: a security release for the Ansible connection plugin that runs tasks inside FreeBSD jails via jexec.
Files pushed into a jail were staged in /tmp on the jail host with the source file's mode (often 0644), so other local users on the host could read them during the transfer. Staging now uses a private 0700 directory.
Thanks to GitHub: manus-pi for the report!
Advisory: https://github.com/chofstede/ansible_jailexec/security/advisories/GHSA-cfm5-946c-m3qx
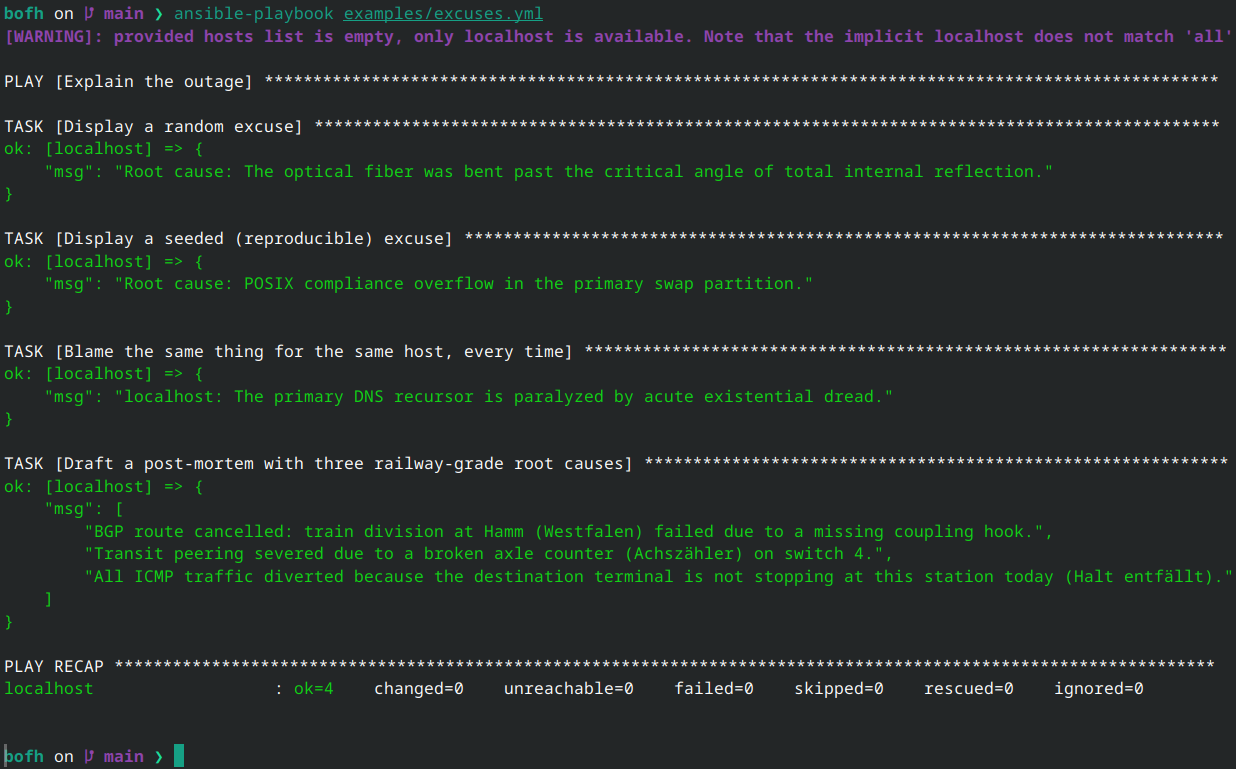
Your playbook failed. Management wants a root cause. You have 30 seconds.
Introducing larvitz.bofh, an Ansible collection that returns Bastard Operator From Hell excuses:
"Root cause: The mainframe tripped over an unhandled SIGSEGV in the automated espresso machine."
Seedable, so each host keeps its story straight. Bonus category: Deutsche Bahn.
https://codeberg.org/Larvitz/ansible-bofh
#Ansible #BOFH #SysAdmin #DevOps #Codeberg #Humor #Linux
For almost a year, my Ansible connection plugin for FreeBSD jails had a jail escape.
A symlink inside a jail, a root-owned mv on the host, and every file transfer could land wherever the jail wanted. Rejecting ".." didn't help at all.
Now it's CVE-2026-55074. Here's the bug, the fix, and what disclosing it looks like when the project has one maintainer.
https://blog.hofstede.it/my-ansible-plugin-had-a-jail-escape-cve-2026-55074/
#FreeBSD #Ansible #InfoSec #CVE #Jails #OpenSource #Security #SysAdmin
How we approach the development and testing of our infrastructure as code, and how it differs at the homelab and professional scales. Plus our Ansible best practices.
https://hybridcloudshow.com/hcs65/
#podcast #iac #homelab #ansible
Alt...
Hybrid Cloud Show artwork
I had a perfectly respectable Red Hat Ansible Automation Platform.
So naturally, I built an Arch Linux Execution Environment, taught pacman to answer to microdnf, and used it to patch RHEL systems.
Surprisingly, it worked.
This is evidence, not a recommendation.
https://blog.hofstede.it/ansible-execution-environment-arch-btw/
New toy for FreeBSD folks who run Ansible: a become plugin for mdo(1), the mac_do(4) counterpart to sudo/doas.
The kernel decides whether the credential transition is allowed, so there is no password, no TTY, no doas.conf, and pipelining just works. Single file, BSD 2-Clause, tested against 15.1-RELEASE.
https://github.com/chofstede/ansible-become-mdo
Feedback welcome, especially from anyone already using mac_do in production.
When talking about open-source virtualization platforms, Proxmox VE is probably one of the first solutions that comes to mind. It combines KVM virtual machines, LXC containers, storage, networking and clustering behind a convenient management interface.
But what if you want to build the same kind of environment on FreeBSD?
This is exactly where Sylve becomes interesting.
https://gyptazy.com/blog/sylve-freebsd-ansible-module-automation/

The #Ansible Bullhorn #234 is out!
Plus new Ansible Core, Antsibull and Ansible Community Package releases. The Ansible 15 roadmap vote accepted, dellemc.unity inclusion requirements violation and community.okd maintenance status discussions.
New collection updates too!
Read more: https://forum.ansible.com/t/the-bullhorn-234/46136
A bug in my Ansible connection plugin needed a real FreeBSD jail to reproduce. So I put three of them on an idle 512 MB free-tier VPS.
With pkgbase, the base userland is just 33 MB. And persistent jails use zero idle processes. Here’s the build, the regression test, and the two sharp edges that cost me twenty minutes:
https://blog.hofstede.it/three-test-jails-on-a-512-mb-free-tier-vps/
As people kept asking for the modules I developed for my @BoxyBSD@bsd.cafe project, I just made them shiny and prepared them for pushing them upstream.
Making the switch easier for people coming from #Proxmox, it uses mostly the same syntax as the Proxmox modules to keep the interface similar. Next to this, they're built in an equal way with a shared authentication module util, to make sure new modules can directly use the same authentication lib.
Currently it comes:
.
├── LICENSE
├── module_utils
│ └── sylve_common.py
├── modules
│ ├── sylve_jail.py
│ └── sylve_vm.py
Ansible is easy to install. A sane, reproducible development environment takes more thought.
My downstream-first setup uses RHEL 10.2, Podman, VS Code Dev Containers, and Red Hat-packaged Ansible Development Tools, while keeping the boundaries between upstream projects, downstream products, development containers, and production Execution Environments explicit.
https://blog.hofstede.it/sane-development-environments-for-ansible-automation-code/

Ich habe mir die letzten Tage Mal die Zeit gegönnt und habe eine (neue) #ansible Rolle auf die "Beine" gestellt: https://github.com/bodsch/ansible-garage
Der Moment wo du in deinem #Ansible Inventory einfach nur eine Versionsnummer änderst und dich danach ein funktionsfähiges, gepatchtes #Forgejo entgegenstrahlt ist schon geil.
Danke an alle die hinter #Forgejo stehen und es weiter entwickeln und an @bodsch für die scm Collection (https://github.com/bodsch/ansible-collection-scm) die einem das leben einfacher macht. :)
The #Ansible Bullhorn #227 is out!
This week's highlights include:
- Paramiko deprecated for network_cli.
- AWX modernization: Ansible Jewel proxy layer.
- ai-forge content development skills update.
- 6 collection updates - check the newsletter for the full list.
Read more: https://forum.ansible.com/t/the-bullhorn-227/45785
The #Ansible Bullhorn #230 is out!
Highlights: Community Execution Environment release.
Plus new Ansible Community Package releases.
New collection updates too.
Read more: https://forum.ansible.com/t/the-bullhorn-230/45889
The #Ansible Bullhorn #231 is out!
Highlights: OpenSuSE Tumbleweed CI image for ansible-test.
Plus new Ansible-Core, Antsibull and Ansible Community Package releases.
New collection updates too.
Read more: https://forum.ansible.com/t/the-bullhorn-231/45948
The #Ansible Bullhorn #233 is out!
Highlights: ansible-core milestone branch bumped, plus EU CRA security concepts for contributors - review open PRs by July 28th!
New collection updates too.
Read more: https://forum.ansible.com/t/the-bullhorn-233/46024