Search results for tag #freebsd
EuroBSDCon 2026 is one month from now! (2026-09-09 - 2026-09-13)
Full program here: https://events.eurobsdcon.org/2026/schedule/
Conference info: https://2026.eurobsdcon.org
Register via https://tickets.eurobsdcon.org/eurobsdcon/brussels/
About the BSD conferences: https://nxdomain.no/~peter/what_is_bsd_come_to_a_conference_to_find_out.html
@eurobsdcon #eurobsdcon #openbsd #netbsd #freebsd #freesofware #libresoftware


 This is my #GoToSocial (on #OpenBSD, on #bhyve, on #FreeBSD) instance, as seen from the garage. Doesn’t it look cute!?

Alt...
An htop screenshot displaying two processes that match a filter.

New 𝗙𝗿𝗲𝗲𝗕𝗦𝗗 𝗦𝘁𝗼𝗿𝗮𝗴𝗲 𝗳𝗼𝗿 𝗢𝗽𝗲𝗻𝗦𝗵𝗶𝗳𝘁 𝘄𝗶𝘁𝗵 𝗗𝗲𝗺𝗼𝗰𝗿𝗮𝘁𝗶𝗰 𝗖𝗦𝗜 [FreeBSD Storage for OpenShift with Democratic CSI] article on vermaden.wordpress.com blog.
https://vermaden.wordpress.com/2026/08/09/freebsd-openshift-democratic-csi/
#verblog #freebsd #linux #openshift #kubernetes #k8s #k3s #csi #miami #storage



Have you starred the #BastilleBSD repository on GitHub yet?
Show your support by becoming a Bastille stargazer!
https://github.com/BastilleBSD/bastille
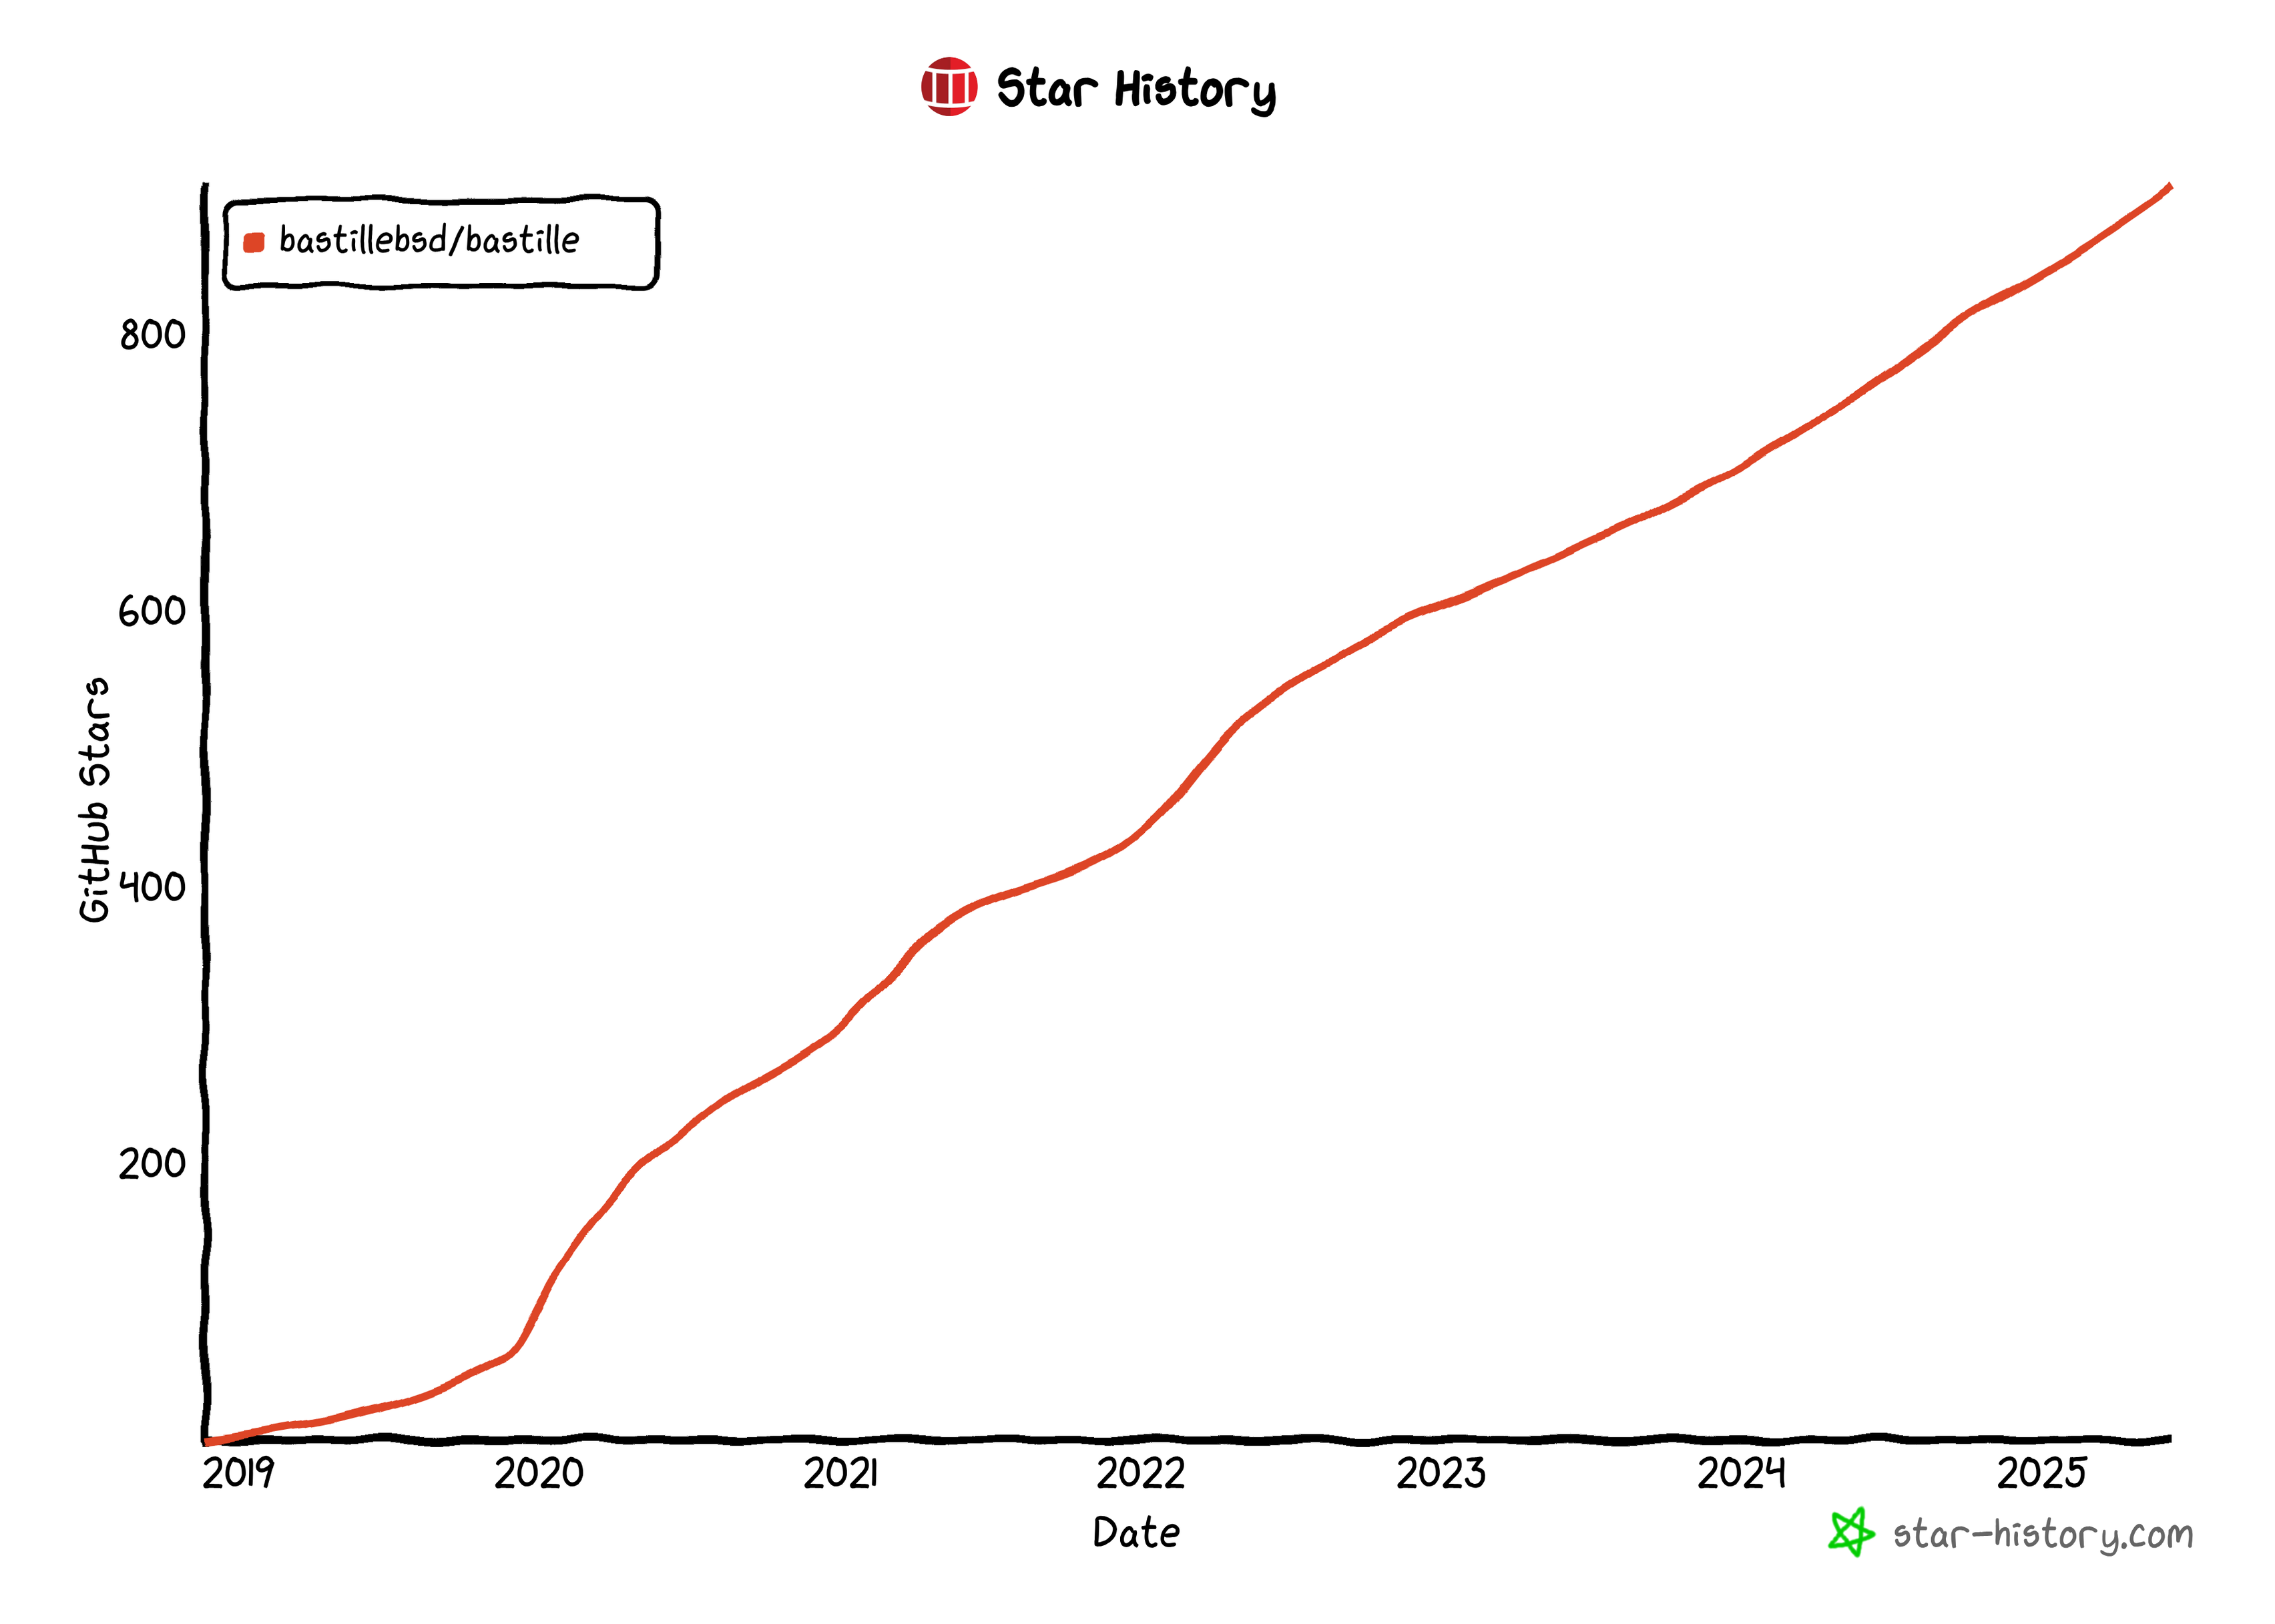
Alt...
Star History for BastilleBSD/bastille repository. The line shows a steady increase from a few in 2019 to over 900 in 2025.
Hey #FreeBSD folks! I have a host that runs jails and also wireguard tunnels on it. It is NOT the router in my network (that's being performed by the ISP-given router).
The network is dual stack and uses both IPv4 and IPv6. This FreeBSD host not only needs to do routing between the private NAT jails but also the wireguard networks, BUT, it still needs to accept router advertisements from the router.
So gateway_enable and ipv6_gateway_enable are right out because if they're enabled, FreeBSD ignores the router advertisements and IPv6 is basically broken on it (it can't router packets)
I still need net.inet.ip.forward=1 in /etc/sysctl.conf because I use Wireguard and PF to NAT traffic out to the internet for one of the wireguard clients. So that is OK to set but I just don't have to enable the gateway options in /etc/rc.conf, right?

New toy for FreeBSD folks who run Ansible: a become plugin for mdo(1), the mac_do(4) counterpart to sudo/doas.
The kernel decides whether the credential transition is allowed, so there is no password, no TTY, no doas.conf, and pipelining just works. Single file, BSD 2-Clause, tested against 15.1-RELEASE.
https://github.com/chofstede/ansible-become-mdo
Feedback welcome, especially from anyone already using mac_do in production.

With Apple phasing out AFP in macOS 27 and Time Capsules officially reaching end-of-life, it's time to move network backups to proper SMB.
If you run a FreeBSD server, you can build a fast, rock-solid, and secure Time Machine target powered by ZFS and Samba - neatly isolated inside a FreeBSD jail using Bastille.
https://it-notes.dragas.net/2026/01/28/time-machine-freebsd-jail/
Keep your macOS backups running smoothly via SMBv3 (with full vfs_fruit support) and full dataset quota control on ZFS!
#FreeBSD #macOS #TimeMachine #ZFS #BastilleBSD #Samba #SysAdmin #Backup #OwnYourData #SelfHosted #BSD #RunBSD #OwnYourData

There is no mention here of etcupdate/merging of etc files... How should that happen now with pkgbase? https://docs.freebsd.org/en/books/handbook/cutting-edge/#pkgbase
At EuroBSDcon 2026:
The night 142 of my servers went up in the clouds. Physically. https://events.eurobsdcon.org/2026/talk/KAEQA8/
Talk by Stefano Marinelli
2026-09-12 11:15:00
To register: https://tickets.eurobsdcon.org/eurobsdcon/brussels/
About EuroBSDcon 2026: https://2026.eurobsdcon.org
@eurobsdcon #eurobsdcon #freebsd #netbsd #openbsd #conference #brussels #bruxelles #freesoftware #libresoftware


Alt...
A screenshot of my Cow ( FVWM for Wayland ) desktop that runs on the River compositor. The wallpaper shows a green meadow with flowers and a girl lying down staring at the sky. In the background are snow peaked mountains. There is a terminal window open with the Cow menus open and a qutebrowser window that is shaded.
When talking about open-source virtualization platforms, Proxmox VE is probably one of the first solutions that comes to mind. It combines KVM virtual machines, LXC containers, storage, networking and clustering behind a convenient management interface.
But what if you want to build the same kind of environment on FreeBSD?
This is exactly where Sylve becomes interesting.
https://gyptazy.com/blog/sylve-freebsd-ansible-module-automation/
We're experimenting with OCI support in Bastille.
Initial testing has successfully created jails using both FreeBSD and Linux container images (requires buildah and jq packages).
If you're interested in this, please check out this PR. Testing is much appreciated.

Found #NVIDIA released new legacy 580 branch of #driver 580.178.04.
Unfortunately, NVIDIA_Changelog included in upstream tarball doesn't seem to have what's changed in this version (same description as previous one), looked for info and found this.
https://docs.nvidia.com/datacenter/tesla/pdf/NVIDIA_Data_Center_GPU_Driver_Release_Notes_580_v12.0.pdf
Anyway, looks fine for RTX A400 installed in Minisforum MS-01 and Quadro P1000 (notebook) in ThinkPad P52. So filed Bug297298 and corresponding review D58674 for upgrading #FreeBSD #ports.
https://bugs.freebsd.org/bugzilla/show_bug.cgi?id=297298
https://reviews.freebsd.org/D58674
Freshly updated: my AS201379 page.
IPv6-only, FreeBSD + FRR, 2a06:9801:1c::/48.
Now with an at-a-glance table (ASN, AS-SET, contacts), full upstream list and new EVIX alongside LocIX Düsseldorf and FogIXP.
Peering policy is open. If we share a presence at any of those three, I'd love to peer: peering@hofstede.it
https://hofstede.it/as201379.html
#BGP #IPv6 #peering #FreeBSD #FRRouting #LocIX #FogIXP #EVIX #AS201379
The redesigned Bastille website now includes a Press page with links to Bastille related content, tutorials and examples.
Do you have a Bastille blog post you'd like to share with the world? Submit it here for inclusion.
Now running this to upgrade (from 15.0 to 15.1) all the jails on this #FreeBSD 15.1 host :
[11:49 zuul dvl ~] % sudo mkjail upgrade -a -v IGNOREME -p n
I don't yet know how best to specify ABI and VERSION on the command line:
pkg -j ${JAILNAME} -oABI=FreeBSD:15:$(uname -p) -oOSVERSION=1501000 upgrade -yr FreeBSD-base
Given my current and recent heavy use of #FreeBSD supplied packages for base, this is interesting:
I'd install it on each internet host I have (given they are each in different data centers).
"Managed FreeBSD pkg caching appliance — proxies pkg.FreeBSD.org to speed up package fetches across image builds and insulate them from upstream rate limits/outages."
https://daemonless.io/images/pkg-cache/
Now I just need that for a plain-vanilla-jail.
When I updated my firewall from #FreeBSD 15.0 to 15.1, I did a:
bectl activate pre-15.1
bectl activate -t default
sudo shutdown -r now
Last night, I patched that host to 15.1-RELEASE-p2 and rebooted.
Afterwards, I was on 15.0 - wtf, did I miss this one in the updates?
`bectl list` revealed it has rebooted into pre-15.1, exactly as instructed...
a quick `bectl activate -t default` and another `shutdown -r now` fixed that.
Remember to activate the BE once you know it's good! ;)
re: https://dan.langille.org/2026/07/17/updating-freebsd-15-0-to-freebsd-15-1-via-pkgbase/
A bug in my Ansible connection plugin needed a real FreeBSD jail to reproduce. So I put three of them on an idle 512 MB free-tier VPS.
With pkgbase, the base userland is just 33 MB. And persistent jails use zero idle processes. Here’s the build, the regression test, and the two sharp edges that cost me twenty minutes:
https://blog.hofstede.it/three-test-jails-on-a-512-mb-free-tier-vps/
Anyone else have issues with tailscaled randomly dying on FreeBSD?
It's a good thing I'm not actually depending on it for connectivity yet, because it can't seem to stay connected.
All #FreeBSD jails in the basement are now running pkgbasify - the process was:
export MYJAIL=unifi01
sudo zfs snapshot data02/jails/$MYJAIL@before.pkgbasify
sudo ./pkgbasify.lua --jail $MYJAIL
sudo joe /jails/$MYJAIL/etc/{master.passwd,group}
sudo jail -rc $MYJAIL
re:
https://dan.langille.org/2026/07/20/running-pkgbasify-on-a-freebsd-15-0-host-to-convert-a-jail/
Next, update those jails to FreeBSD 15.1
As people kept asking for the modules I developed for my @BoxyBSD@bsd.cafe project, I just made them shiny and prepared them for pushing them upstream.
Making the switch easier for people coming from #Proxmox, it uses mostly the same syntax as the Proxmox modules to keep the interface similar. Next to this, they're built in an equal way with a shared authentication module util, to make sure new modules can directly use the same authentication lib.
Currently it comes:
.
├── LICENSE
├── module_utils
│ └── sylve_common.py
├── modules
│ ├── sylve_jail.py
│ └── sylve_vm.py

Current status: updating #FreeBSD 15.0 jails to FreeBSD 15.1
That consists of two main steps:
* pkgbasify
* mkjail upgrade -j $MYJAIL
I've modified my local copy of mkjail to use pkg, not freebsd-update.
IMPORTANT NOTE ABOUT TODAY'S RELEASE!
This version makes a minor but significant change in the way it handles port redirection (RDR) to jails. If you're using RDR to any jails, you'll need to add one line to one file.
Update your `/etc/pf.conf` by adding:
`anchor bastille/*`
at the beginning of the filtering section.
See https://bastille.readthedocs.io/en/latest/chapters/networking.html#etc-pf-conf for an example.
This provides improved filtering for incoming traffic before it hits the jail.
Also noted in pkg-message.
Latest 𝗩𝗮𝗹𝘂𝗮𝗯𝗹𝗲 𝗡𝗲𝘄𝘀 - 𝟮𝟬𝟮𝟲/𝟬𝟴/𝟬𝟯 (Valuable News - 2026/08/03) available.
https://vermaden.wordpress.com/2026/08/03/valuable-news-2026-08-03/
Past releases: https://vermaden.wordpress.com/news/
#verblog #vernews #news #bsd #freebsd #openbsd #netbsd #linux #unix #zfs #opnsense #ghostbsd #solaris #vermadenday

Some time ago, I started looking for a Braille display to help implement Braille display support in #FreeBSD
Update: I managed to get a used one from the United States, and it should arrive by the end of the month.
If your country has websites that sell used items, I'd really appreciate it if you could keep an eye out for affordable Braille displays and let me know if you find any. Thank you!
#accessibility #braille #UNIX #opensource #assistiveTechnology
Practical FreeBSD hint: Want to see how much traffic your PF host handles via IPv4 vs IPv6?
pfctl -si | awk '
/Bytes (In|Out)/ {v4+=$3; v6+=$4}
END {
t=v4+v6
printf "IPv4: %.2f GiB (%.1f%%)\nIPv6: %.2f GiB (%.1f%%)\n",
v4/2^30, 100*v4/t, v6/2^30, 100*v6/t
}'
Example from one of my servers:
IPv4: 0.22 GiB (42.1%)
IPv6: 0.30 GiB (57.9%)
The counters cover traffic since PF was last started or the host rebooted.
Also: "in" is a reserved keyword in awk. Ask me how I found out. 😅
https://codeberg.org/thomasadam/cow
#Wayland #fvwm #CoW #RiverWM #FreeBSD


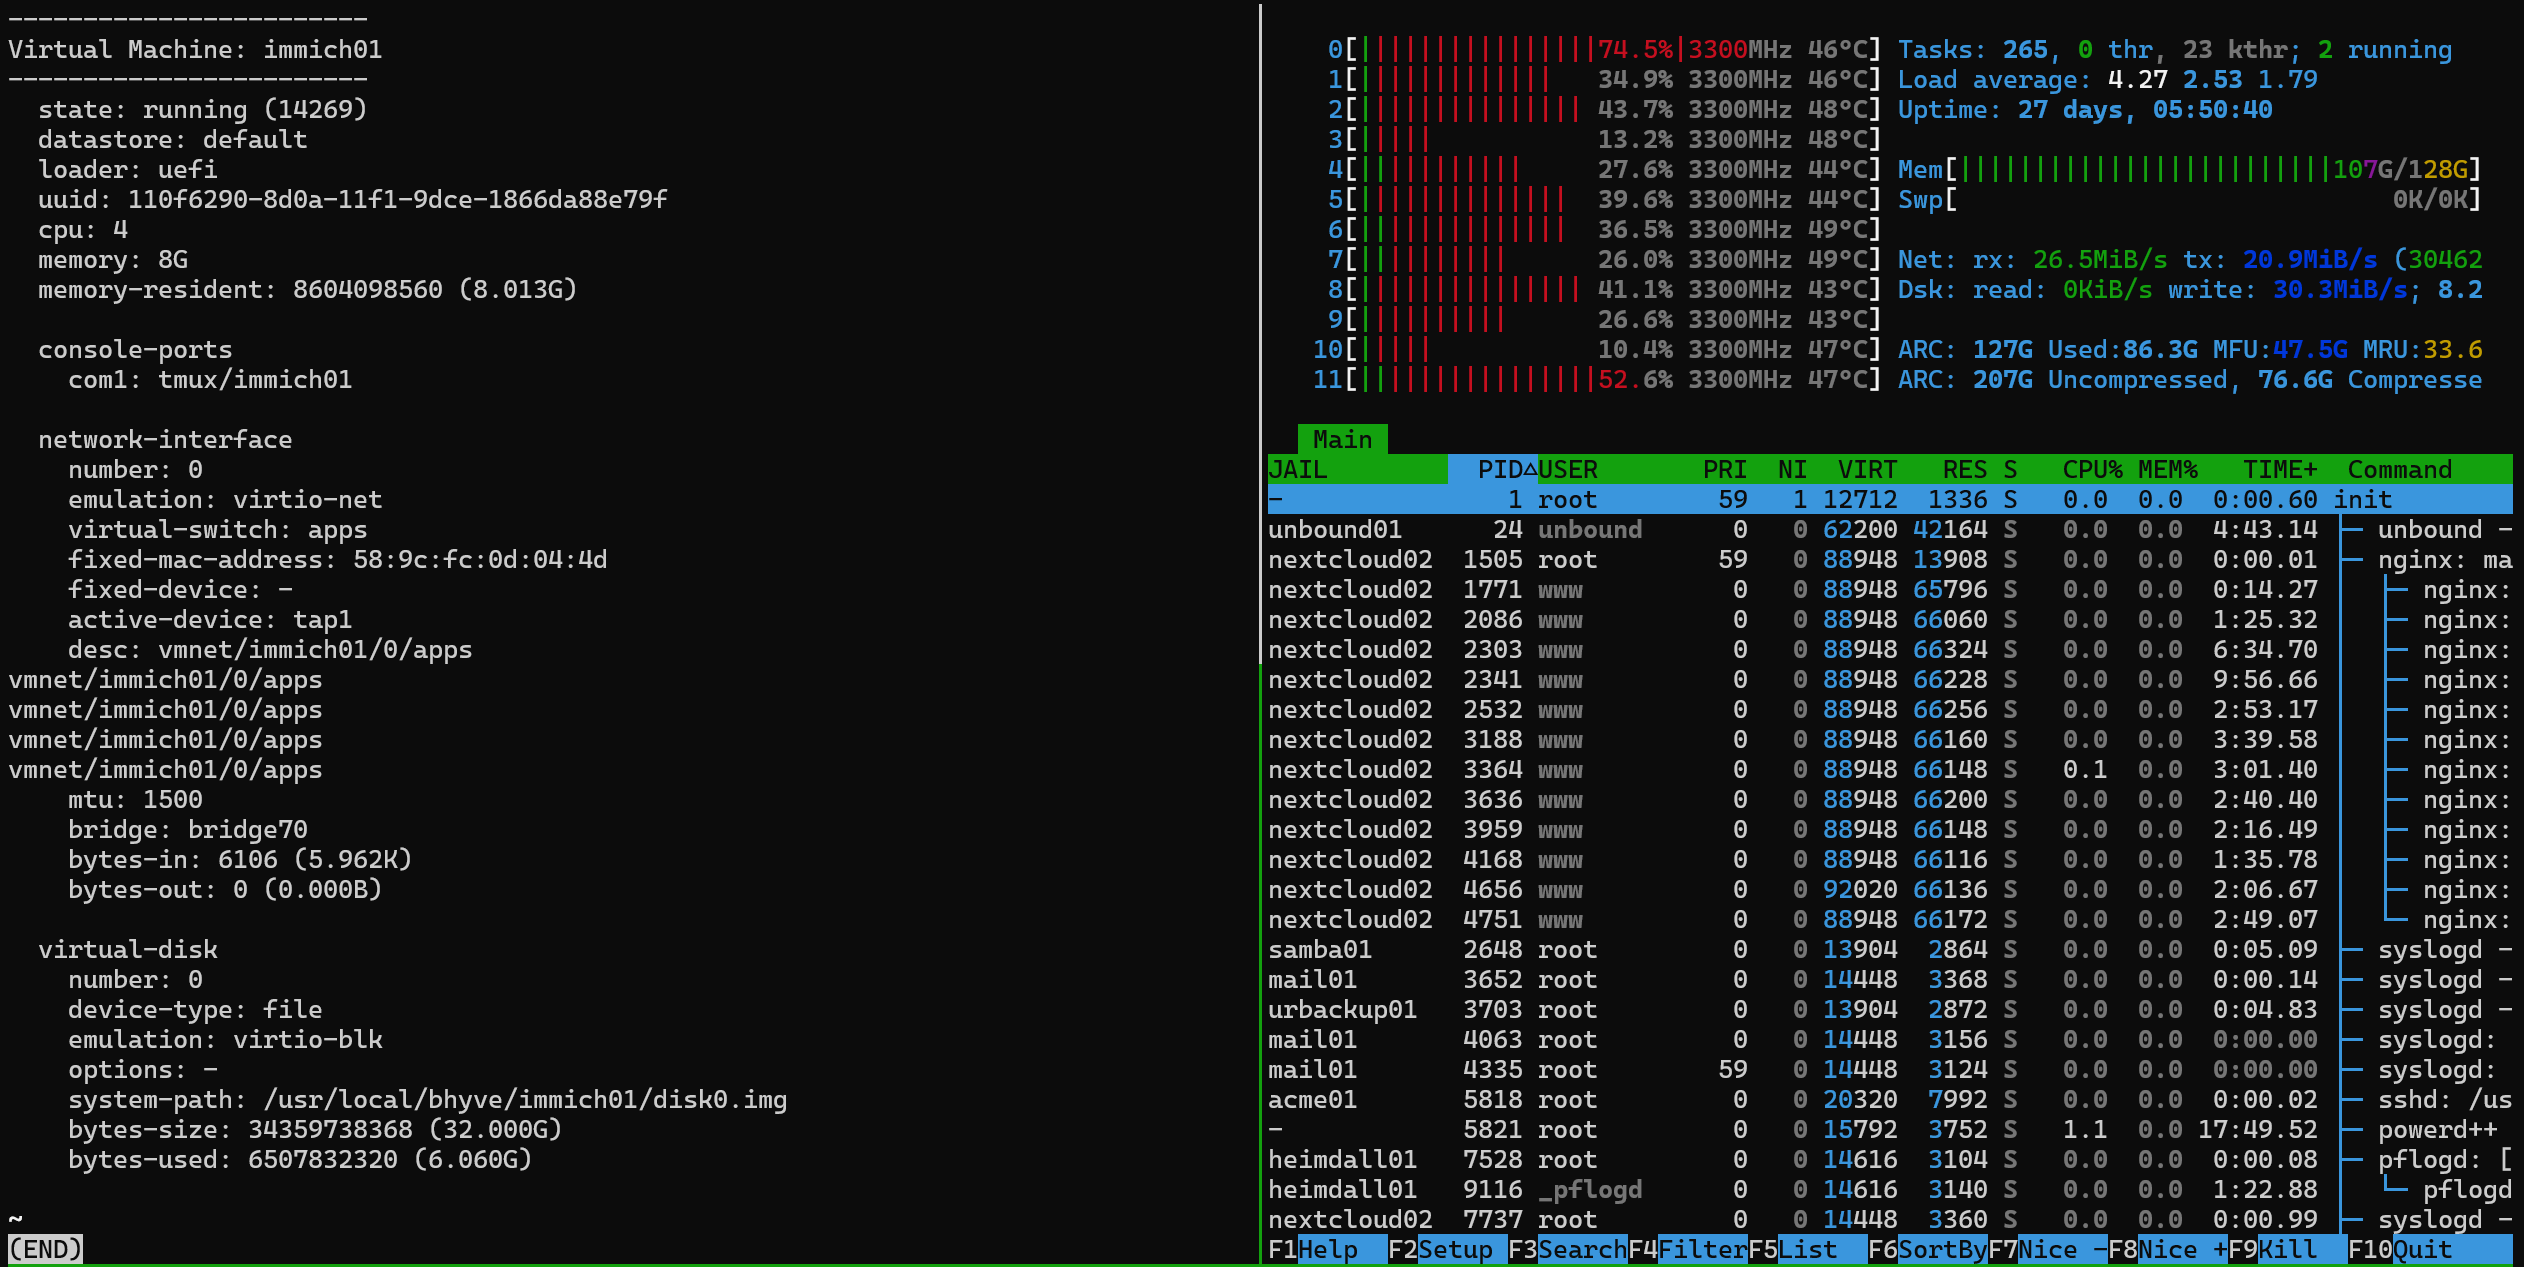
Today I installed #Immich in a Docker container on Debian inside a #Bhyve VM on my #FreeBSD home server and trying it out right now by backing up my phones pictures to it.
All that's left for me to do now is wait until the upload is finished, which is the hardest part.😅
Alt...
Screenshot of my vm-bhyve Debian VM on the left and htop on the right while packing up all of my phones pictures to it.

Happy Sysadmin Appreciation Day
To all the sysadmins quietly keeping the lights on, we salute you.
#Sysadmin #FreeBSD #Linux #OpenBSD #BastilleBSD
Alt...
A "UNIX System Park" t-shirt, with a silhouette of characters Lex and Tim. Lex is saying, "IT'S A UNIX SYSTEM. I KNOW THIS!" and then the text, "REBOOTING SYSTEM...", in a parody of the 'Jurassic Park' logo.