Search results for tag #freebsd

I've asked Claude for some starting points for ports which obtain `PORTVERSION` from outside their `Makefile` - specifically `Mk/bsd.default-versions.mk` in this case. There are others, but this is where I started.
The current code, untested and unreviewed, sits here:
https://github.com/FreshPorts/DefaultVersions
The first issue is at:
https://github.com/FreshPorts/DefaultVersions/issues
Pull requests most welcome. Let's see if we can complete this as a group. I don't want to do it myself.

Reminder that you can now find Bastille on Reddit.
https://reddit.com/r/BastilleBSD
Alt...
BastilleBSD just hit 50 weekly visitors. Things are getting cozy here. Share this with the community to celebrate your milestone!
This week we celebrate the core team and the contributors that have shaped Bastille into the project we know today.
https://bastillebsd.org/about/team/
Thanks to everyone following and thanks to everyone that has contributed.
Anyone running #FreeBSD and #unbound (DNS resolver) and finding unbound doesn't actually start after a reboot?
The init script has:
# PROVIDE: unbound
# REQUIRE: FILESYSTEMS defaultroute netwait resolv
# BEFORE: NETWORKING
# KEYWORD: shutdown
However, unbound needs to listen on an interface or IP. Why have the script run before networking and yet "require" defaultroute? This makes no sense.
This morning a new non-production release of mkjail-0.2.0 was created. It is not available in the #FreeBSD ports tree.
Here's my first attempt:
[11:49 tallboy dvl ~] % sudo mkjail update -a
Updating all jails...
Updating ns1 jail...
freebsd-update is incompatible with the use of packaged base. Please see
https://wiki.freebsd.org/PkgBase for more information.
[11:49 tallboy dvl ~] % sudo mkjail update -a -b
Updating all jails...
Updating ns1 jail...
and the next attempt, by specifying `-b`
[11:49 tallboy dvl ~] % sudo mkjail update -a -b
Updating all jails...
Updating ns1 jail...
Updating FreeBSD-base repository catalogue...
FreeBSD-base repository is up to date.
FreeBSD-base is up to date.
Updating FreeBSD-base repository catalogue...
FreeBSD-base repository is up to date.
FreeBSD-base is up to date.
Checking for upgrades (11 candidates): 100%
...
On the next host, I'll set PKGBASE in mjkail.conf

One of today’s tasks: migrating an old Ubuntu server hosting around 15 WordPress sites to a FreeBSD server, with Caddy acting as a reverse proxy in its own jail, one jail per WordPress instance, and a shared database in yet another jail.
Yesterday I configured Caddy to reverse proxy all the domains while still pointing to the old server. That allowed the customer to update the DNS records in advance, while I could migrate each site one by one and simply switch the upstream in Caddy as soon as it was ready.
Zero downtime. Just a reload.
I asked only for one thing: freeze everything this morning, so a colleague asked the customer not to make any changes to the websites after 7 today.
Ack.
So I go to clone one of the sites… and notice the customer published a totally deferrable post at 9.
Which, of course, means I now get to resync everything.
Ah, the joys of working "behind the scenes". 😆
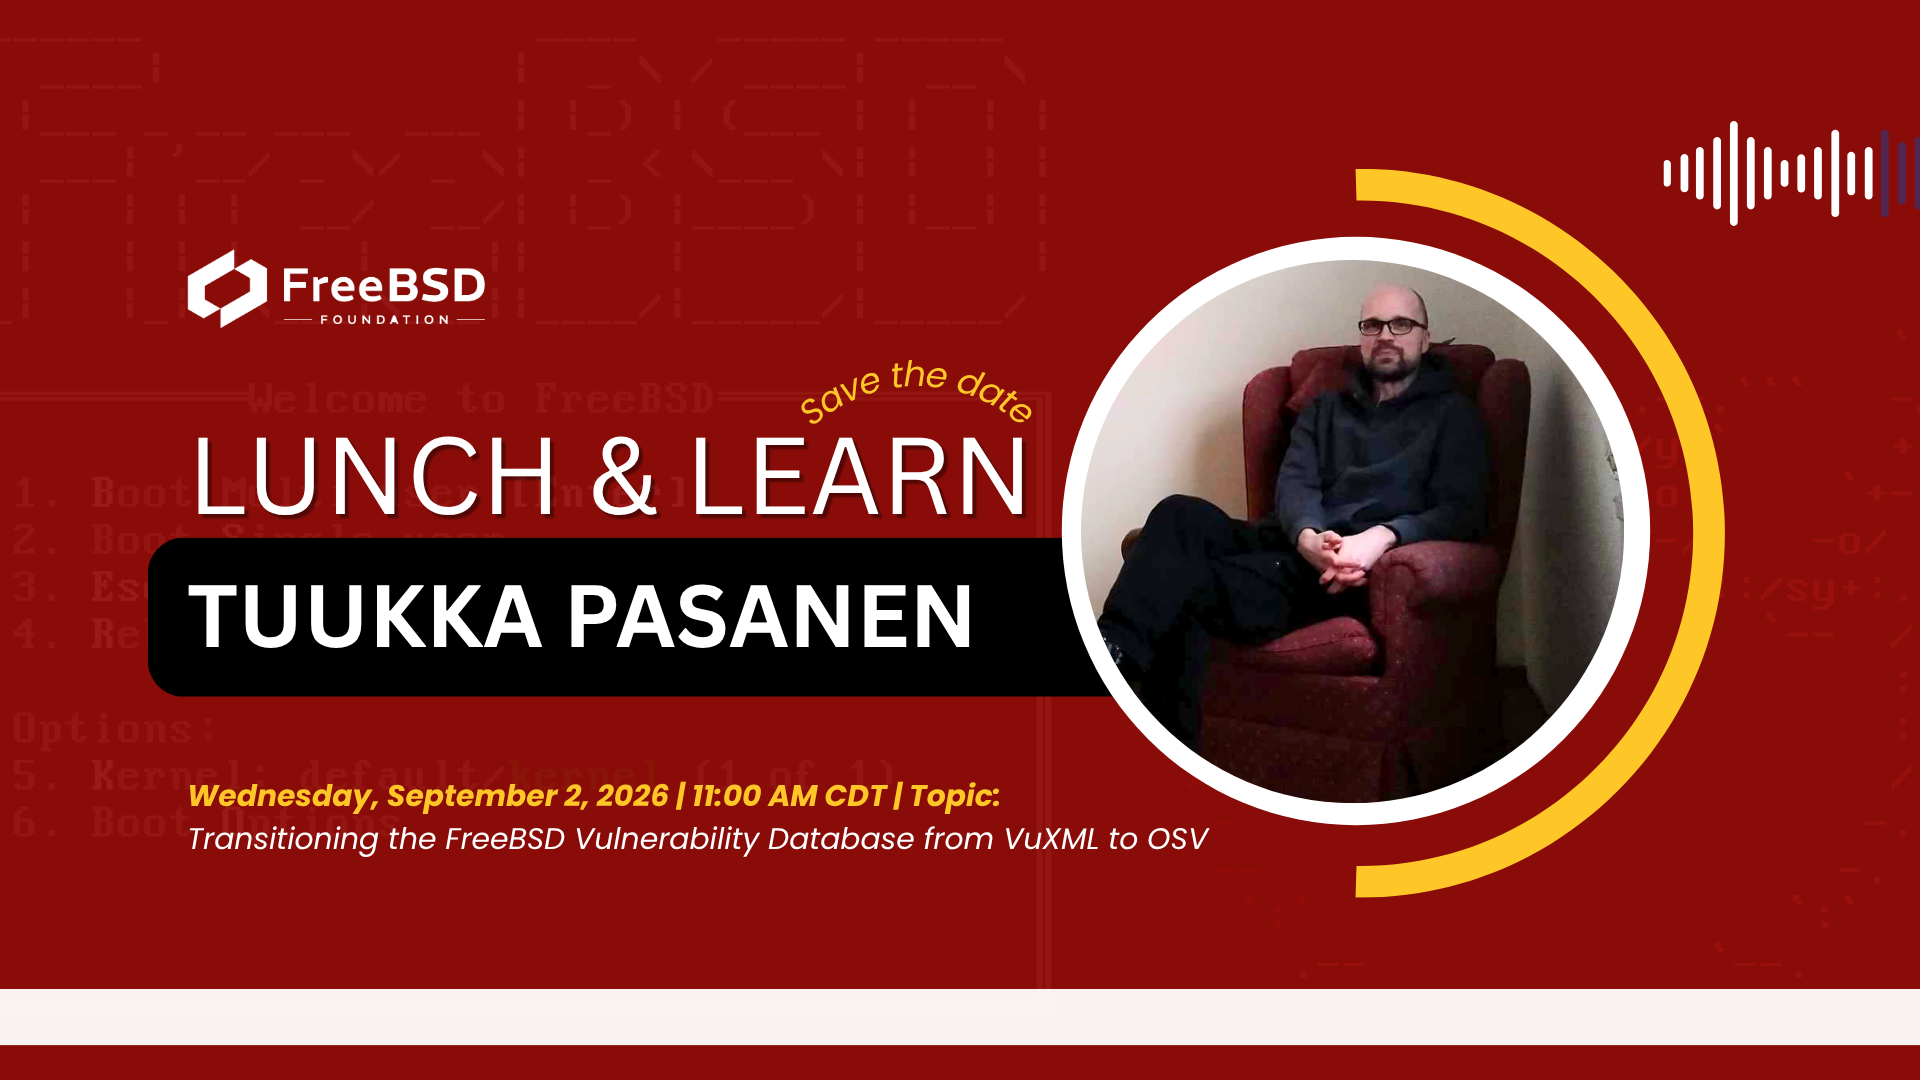
Join Tuukka Pasanen today for our next Lunch & Learn as he explores the work underway to transition the FreeBSD Vulnerability Database from VuXML to OSV, a widely used vulnerability format that officially supports FreeBSD in its schema.
📅 Wednesday, September 2 | 11:00 AM CDT / 16:00 UTC
Speaker: Tuukka Pasanen | FreeBSD Foundation Lunch & Learn
YouTube Live Link:
https://buff.ly/m5XZp1S
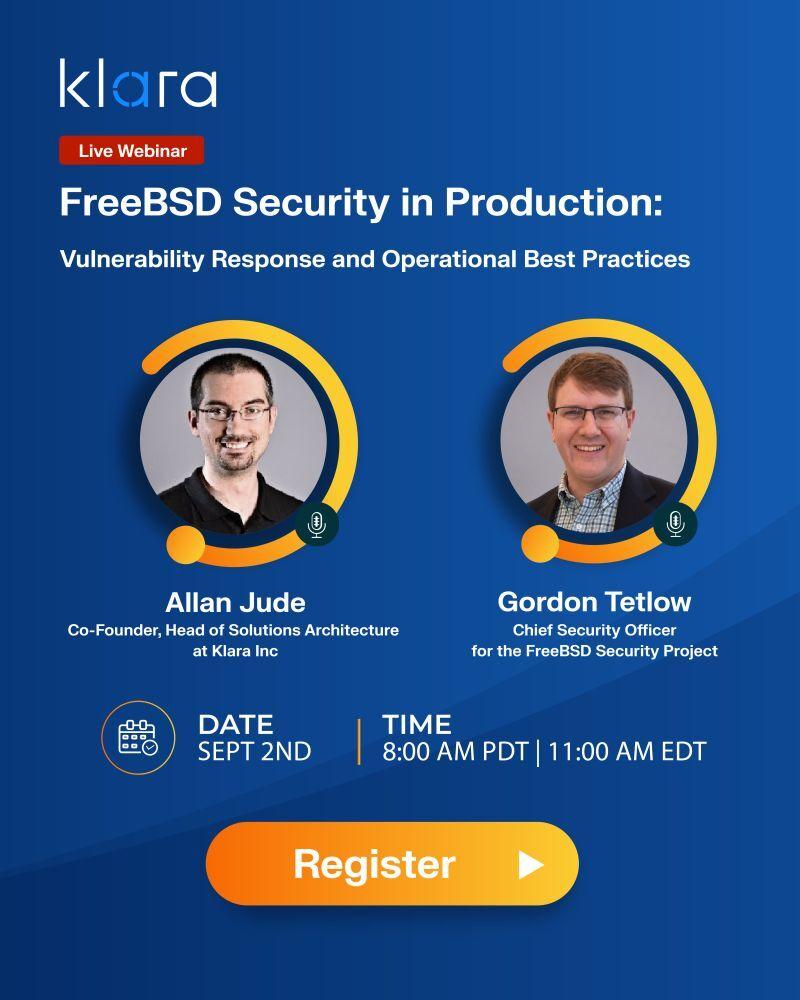
Join Klara's Allan Jude and FreeBSD Security Officer Gordon Tetlow for a technical webinar on securing production FreeBSD systems. Klara Inc
In this session, you'll learn about FreeBSD's security features, best practices for securing production environments, how the FreeBSD Security Team responds to vulnerabilities and publishes security advisories, and common operational mistakes that can increase risk.
📅 September 2, 2026
🕚 11:00 AM EDT
Register here: https://klarasystems.com/webinars/freebsd-security-production-vulnerability-response-best-practices/
Monthly reminder to periodically check your bastille.conf for updates or new entries from the sample config:
cd /usr/local/etc/bastille
diff -u bastille.conf bastille.conf.sample
We try to keep config updates to a minimum, but sometimes they are required.
Current status: Getting help from Claude (via Anthropic free open source credits) to investigate #FreeBSD ports which get their PORTVERSION not from the Makefile.
Some ports obtain their version from Mk/*
Some light background reading for you: https://github.com/FreshPorts/freshports/issues/659

Also going to try #Librewolf instead of #Qutebrowser to see how I go on my #FreeBSD #ThinkPad .
Hey #IPv6 folks: If I do NOT have a /64 assigned to me and only have a single IPv6 assigned, am I better off adding fd00::/7 addresses to the jails and then NAT'ing to them like I do with the IPv4 addresses?
I don't think I have any other kind of choice here.

Latest 𝗩𝗮𝗹𝘂𝗮𝗯𝗹𝗲 𝗡𝗲𝘄𝘀 - 𝟮𝟬𝟮𝟲/𝟬𝟴/𝟯𝟭 (Valuable News - 2026/08/31) available.
https://vermaden.wordpress.com/2026/08/31/valuable-news-2026-08-31/
Past releases: https://vermaden.wordpress.com/news/
#verblog #vernews #news #bsd #freebsd #openbsd #netbsd #linux #unix #zfs #opnsense #ghostbsd #solaris #vermadenday
Manpage Monday: bastille console
Need a shell inside a jail? Step right in.
Console into myjail
> bastille console myjail
Enter as a specific user
> bastille console myjail bob
Jail stopped? -a starts it first, then drops you in:
> bastille console -a myjail bob
See `man bastille-console` for more details.
https://git.smithies.me.uk/freebsd-thinkpad-p14s-amd-dotfiles/tree/.kshrc
Using #PostgreSQL? pgbot looks interesting.
https://github.com/pgrundev/pgbot
It was just added to the #FreeBSD ports tree.

At 10:15 I added a gently condescending toast for IPv4-only visitors. It called ipify, which felt inappropriate for someone running an ASN.
By 13:27 I had built a Rust/Axum IP service, put it behind Caddy, added MaxMind, three DNS names, trusted-proxy handling, an rc.d service, and a dedicated dual-stack FreeBSD VNET jail.
The toast looks exactly the same.
https://blog.hofstede.it/i-wanted-an-ipv4-toast-and-accidentally-built-an-ip-service/
It started as a gag: a tiny popup telling IPv4 visitors that their provider hasn't yet discovered 1998.
To do that honestly I needed something to echo the client address.
Using ipify felt wrong when you run your own AS. So now it's a service. 🙃
curl https://ip.hofstede.it
curl https://v6.ip.hofstede.it/json
curl https://v4.ip.hofstede.it/asn
One Rust binary, server-rendered, zero JavaScript.
I’m starting to get pissed off at #FreeBSD lack of quality. Upgrading from 13 to 15 broke a basic lib that I had to manually copy from a boot disk to restore my system. Now, someone decided to change adguardhome package in a way that it completely fucks existing installations when upgrading without absolutely no warning.
FreeBSD used to be known exactly for shit like this NOT happening. What’s changing in this project? Why is it so similar to Linux now, that an upgrade breaks every damn thing?
I don't get it. I configured portacl on the host. Tested on the host and it allows me to bind to the privileged ports I configured. Tried on the jail. Does not work. Same user ID. I don't understand what's missing. #FreeBSD


#WeekendLife as the family is away I am going out for pizza, followed by tiramisu and either a grappa or a limoncello to help me make it home safely. Then I intend to binge-watch 4 weeks of Silo and Sugar on Apple TV, and a couple of episodes of The Order (bad) and The Last Airbender (good) that I've been watching with the kids, that I missed out on.
Then I am going to hack all Saturday and Sunday for funsies on some #FreeBSD stuff, hopefully without any interruption apart from going to a local Asian restaurant for dinner.
In FreeBSD I've been working on mostly ports:
- adding arm64 support to tailwindcss4
- investigating https://nodejs.org/api/single-executable-applications.html so that we can package nodejs apps as a "single" archive binary rather than 200k+ individual files. This has turned out to be a very enlightening and horrifying rabbit hole that I am not yet out ot
- porting lua-http and its dependencies
- which requires lua-cqueues which breaks libuv in weird ways that causes kresd (Knot3 DNS Resolver) to break
- fixing simplomon to run on FreeBSD CURRENT
- tweak some podman tooling for fun
- finally update part 2 of my Containers contribution to the HandBook
- do some releng testing of the upcoming 14.5 release to make sure all the 🦆🦆🦆 are in a row
- try to clean up my flua contribs for FreeBSD src for review before EuroBSDcon
[thank-you for your attention to this matter]
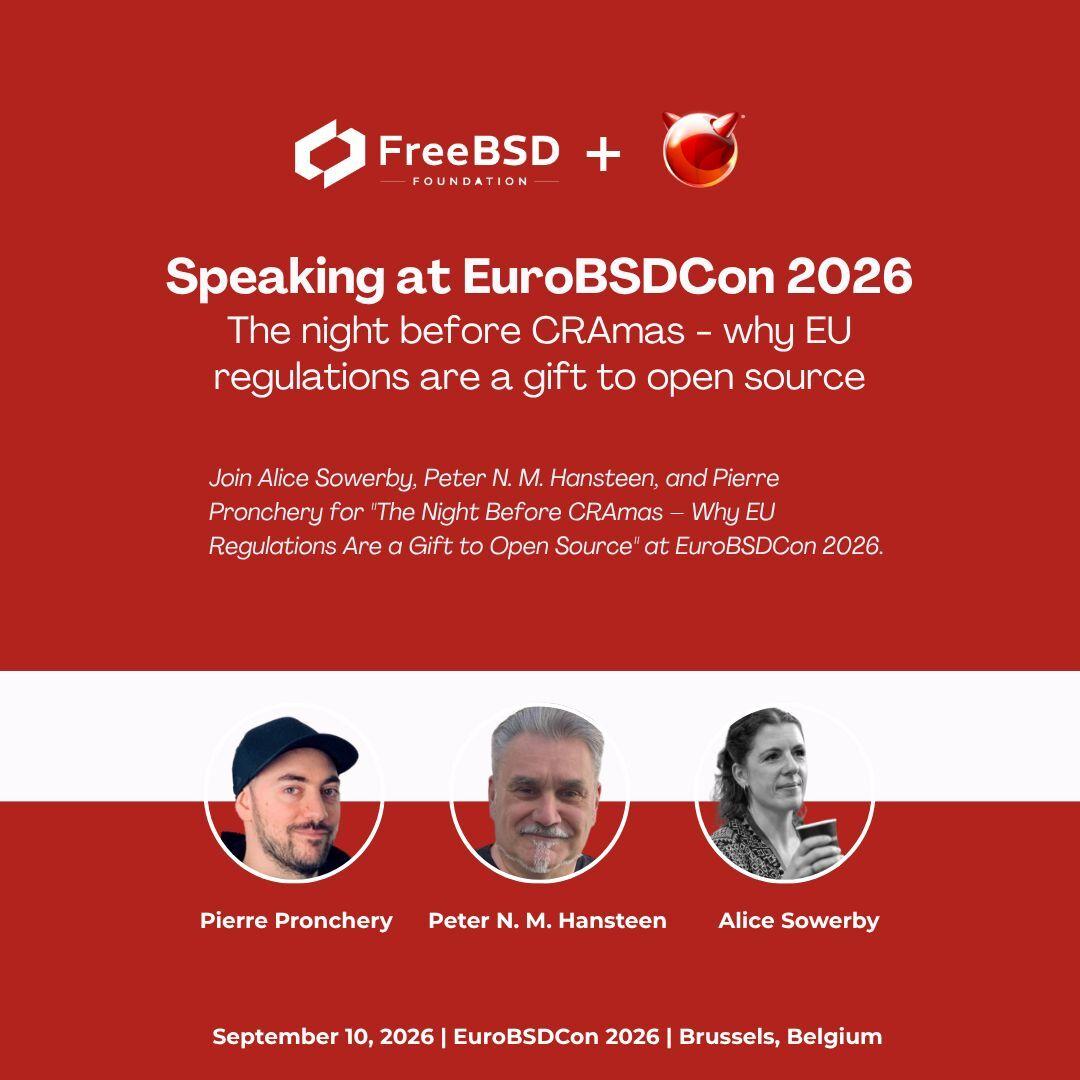
The EU Cyber Resilience Act is bringing new requirements for software, and open source developers, organizations, and businesses need to be ready.
On September 10 at #EuroBSDCon2026, join Alice Sowerby, Peter Hansteen, and Pierre Pronchery for the full-day tutorial, “The Night Before CRAmas – Why EU Regulations Are a Gift to Open Source.”
📅 September 10, 2026
📍 EuroBSDCon 2026 | Brussels, Belgium
Learn more and register:
https://events.eurobsdcon.org/2026/talk/RER8UZ/
New 𝗟𝗲𝗻𝗼𝘃𝗼 𝗫𝗖𝗹𝗮𝗿𝗶𝘁𝘆 𝗔𝗱𝗺𝗶𝗻𝗶𝘀𝘁𝗿𝗮𝘁𝗼𝗿 𝗶𝗻 𝗙𝗿𝗲𝗲𝗕𝗦𝗗 𝗕𝗵𝘆𝘃𝗲 𝗩𝗠 [Lenovo XClarity Administrator in FreeBSD Bhyve VM] article.
https://vermaden.wordpress.com/2026/08/28/lenovo-xclarity-administrator-in-freebsd-bhyve-vm/
#verblog #freebsd #bhyve #linux @lenovo